Microsoft Intune consolidates a large portion of its management features in the Intune admin center. This is where you manage devices and applications, configure policies, monitor compliance, and access reports as well as tenant settings.
In this article, we will guide you through the most important areas of the Intune admin center, show you where to find specific features, and highlight what matters most for day-to-day management.
The most important things in brief
- Centralized administration: The Intune Admin Center provides a unified interface for managing Windows, Android, iOS, and macOS devices.
- Structured navigation: Devices, apps, users, policies, and groups can be quickly found and managed from separate areas.
- Compliance and security: Compliance policies and conditional access ensure that only secure devices access corporate resources.
- Flexible configuration: Dashboards and portal settings can be customized — ideal for different roles or teams.
- Efficient troubleshooting: With integrated troubleshooting tools and support requests, technical issues can be quickly analyzed and resolved.
As an experienced partner SOFTTAILOR helps companies implementing, optimizing and operating Microsoft Intune. From initial concept through technical implementation to ongoing operation — including software packaging, policy design, and support processes.
1. What is the Microsoft Intune admin center?
The Microsoft Intune admin center is a cloud-based management interface for Unified Endpoint Management (UEM) and a core component of the Microsoft Intune product. It serves as a central web portal for managing devices, applications, and policies. It provides IT administrators with direct access to all the features required for comprehensive and secure endpoint management—for both company-owned and personal devices running Windows, iOS, Android, and macOS.
The portal provides features such as:
- Device management
- Software distribution and management
- Enforcement of security policies
- Monitoring device compliance
- Integration with other Microsoft cloud services (e.g., Microsoft 365, Microsoft Entra ID, Microsoft Defender)
Thanks to its cloud architecture, management tasks can be performed from any location. Intune thus supports the modern, hybrid workplace and reduces operational overhead through automated processes, policy-based management, and a centralized overview.
2. Access and requirements
The Microsoft Intune admin center can be accessed via the web address https://intune.microsoft.com . Access requires a Microsoft Entra ID account (formerly Azure Active Directory) with the appropriate permissions. Authentication is typically handled via Entra ID and can be secured by mechanisms such as multi-factor authentication (MFA) or Conditional Access can be extended.
Technical and organizational requirements:
- Microsoft 365 or Intune subscription with an active license
- Microsoft Entra ID: for identity management and group control
- Supported web browser: e.g., Microsoft Edge, Google Chrome, Mozilla Firefox
- At least one assigned administrator role in Intune (e.g., Intune Administrator, Helpdesk Operator, Policy and Profile Manager)
Role-based access control (RBAC) allows for granular permission management. For example, one administrator can be responsible solely for app deployment, while another manages only device settings. Furthermore, it is recommended to use Conditional Access policies to grant or block administrator access based on device state, user location, or network context.
Once logged in, administrators have direct access to all central management functions via the dashboard—no additional client installation required.
Key navigation areas at a glance:
- Devices: Manage registered endpoints, including device groups, operating system status, assignments, and policies. Search, filter, and manage devices via remote actions (e.g., wipe, restart).
- Apps: Control the application lifecycle – from deployment and updates to uninstallation. Supports Microsoft Store apps, Win32 applications, LOB apps (Line of Business), and web links.
- Policies: Centralized management of configuration profiles (e.g., Wi-Fi, VPN, email), compliance policies, endpoint protection settings, and device restrictions.
- Users & Groups: Overview and management of Entra ID users and groups for targeted policy assignment and permission control.
- Reports: Access predefined and custom reports to analyze compliance, app installations, device status, and security policies.
- Tenant Administration: Tenant-level settings, such as license overview and connection status for Microsoft Defender or Endpoint Analytics.
Each of these areas can be accessed via the left-hand navigation menu. Within the modules, filters, search functions, and context-sensitive actions streamline daily tasks—especially in large environments with many devices and user groups.
{{anwendungen-bereitstellen="/en/dev/components"}}
3. Tour of the Microsoft Intune Admin Center
1. Sign-in and Home Page
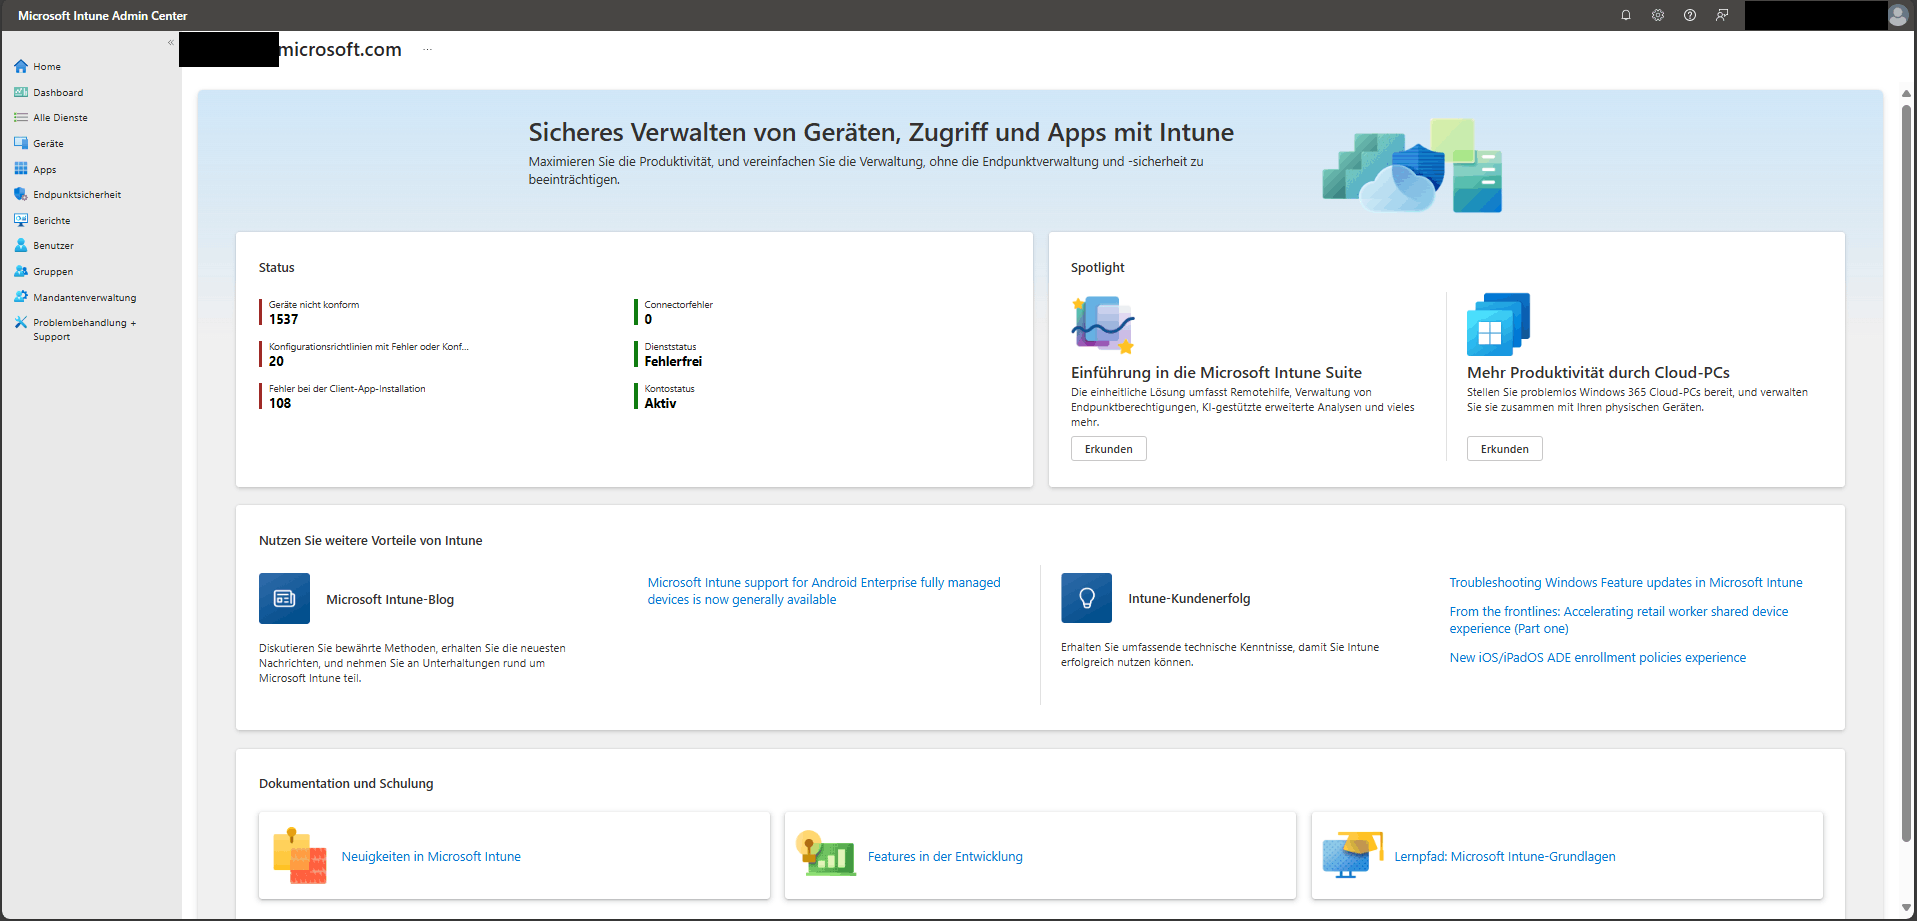
After signing in, the Intune Admin Center home page opens by default. It provides a visual snapshot of your tenant status, such as device compliance, recent notifications, and links to frequently used areas. This view is particularly helpful for identifying potential action items at a glance.
2. Dashboard View
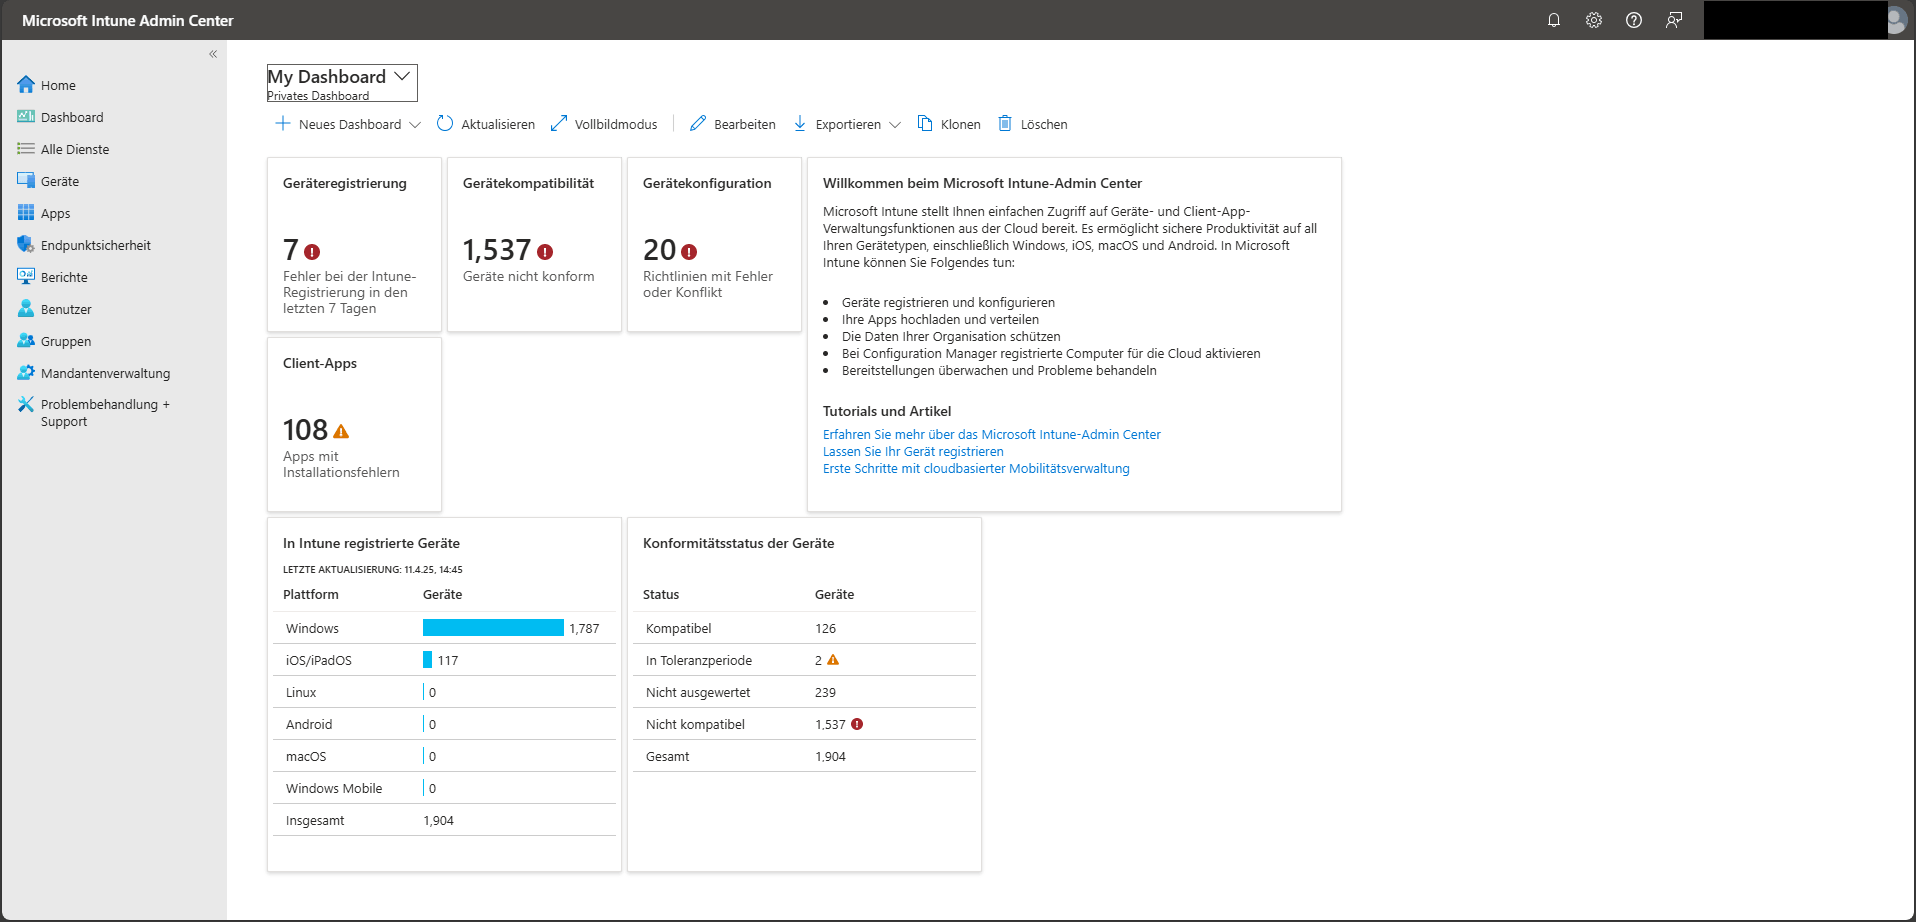
The dashboard provides an aggregated overview of your Intune tenant's health. Here, administrators can find information on enrolled devices, installed applications, policy status, and compliance results. This area is ideal for a quick status assessment – for example, before a daily stand-up or when preparing for audits.
3. Devices Section
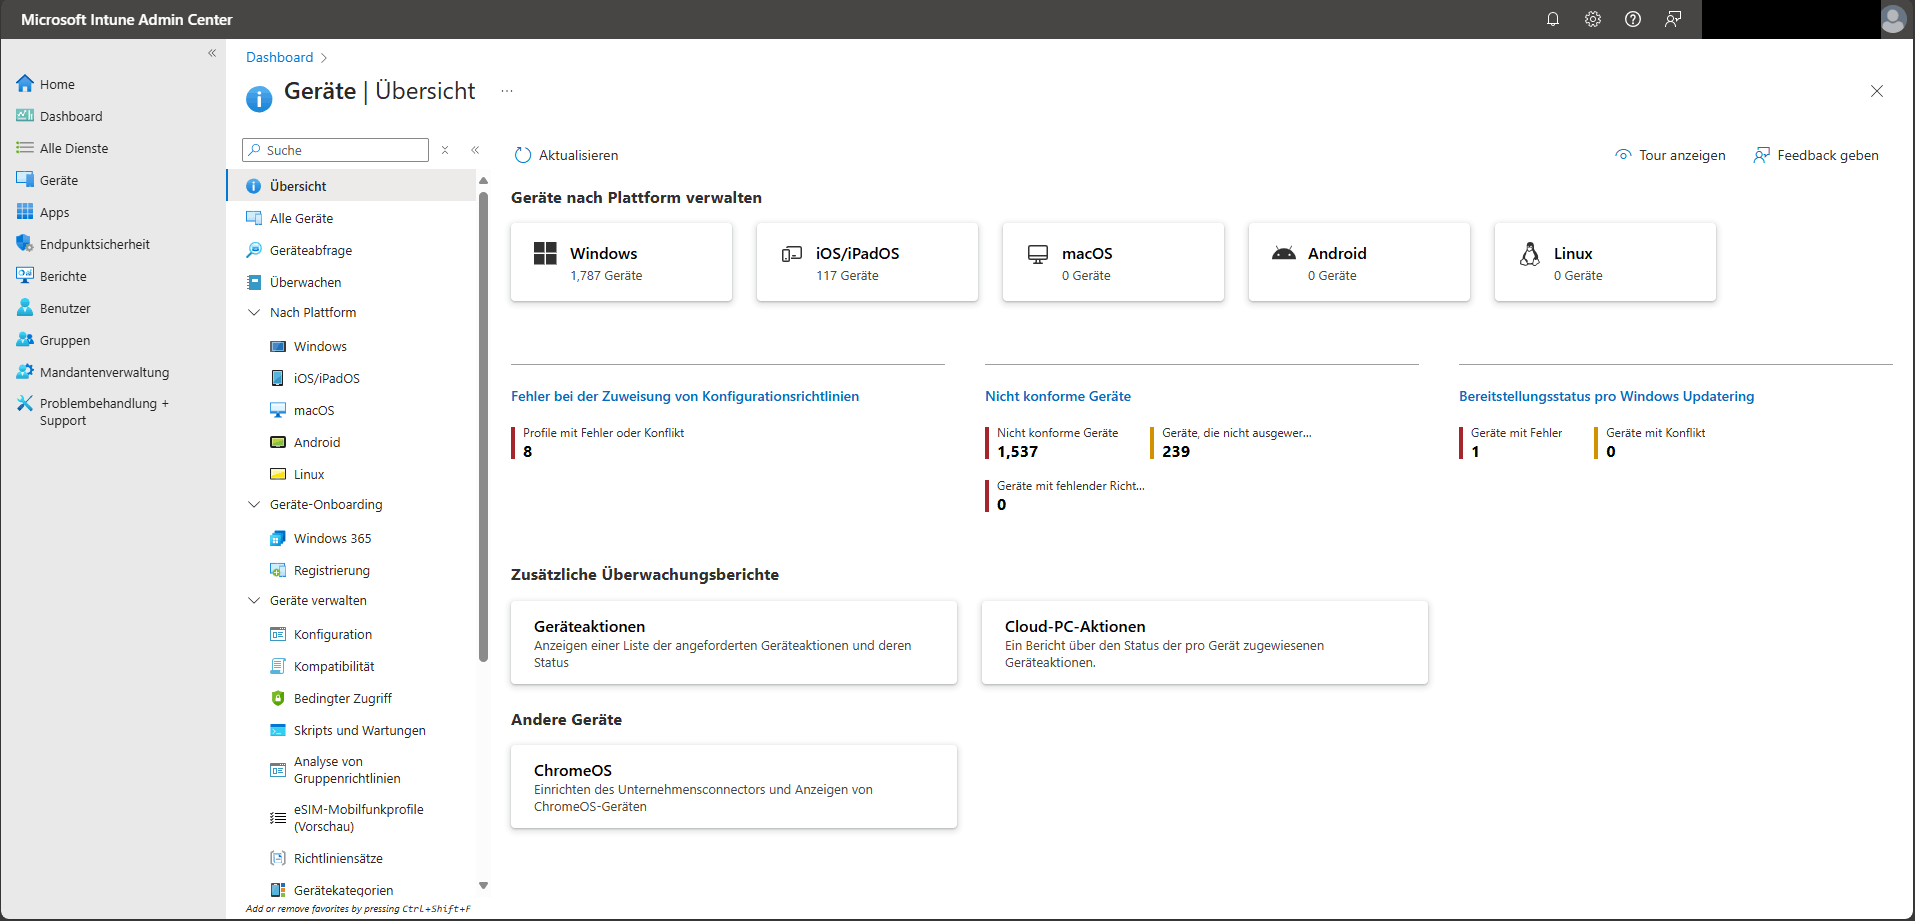
In the Microsoft Intune Admin Center navigation menu, under the "Devices" section, you will find a central overview of all devices enrolled in your tenant. This area provides essential information for the daily management and monitoring of endpoints.
The "Devices – Overview" page includes the following key information, among other things:
- Number of managed devices by platform (e.g., Windows, iOS/iPadOS, Android)
- Errors or conflicts in configuration policies
- Non-compliant devices based on compliance requirements
- Update status of Windows devices, including potential errors
Note: If you previously used Intune via the Azure portal, you can now find this information directly in the Intune Admin Center.
4. Device enrollment methods
Intune supports a variety of enrollment types that should be selected based on device type (Windows, macOS, iOS/iPadOS, Android), ownership status (personal vs. corporate), and management goals. The most important methods include:
- Windows Autopilot for zero-touch provisioning
- Apple Automated Device Enrollment (ADE) for company-owned Apple devices
- Android Enterprise incl. zero-touch
- Manual enrollment for testing or special cases
The choice of method affects, among other things, the depth of management and the level of automation.
5. Conditional Access
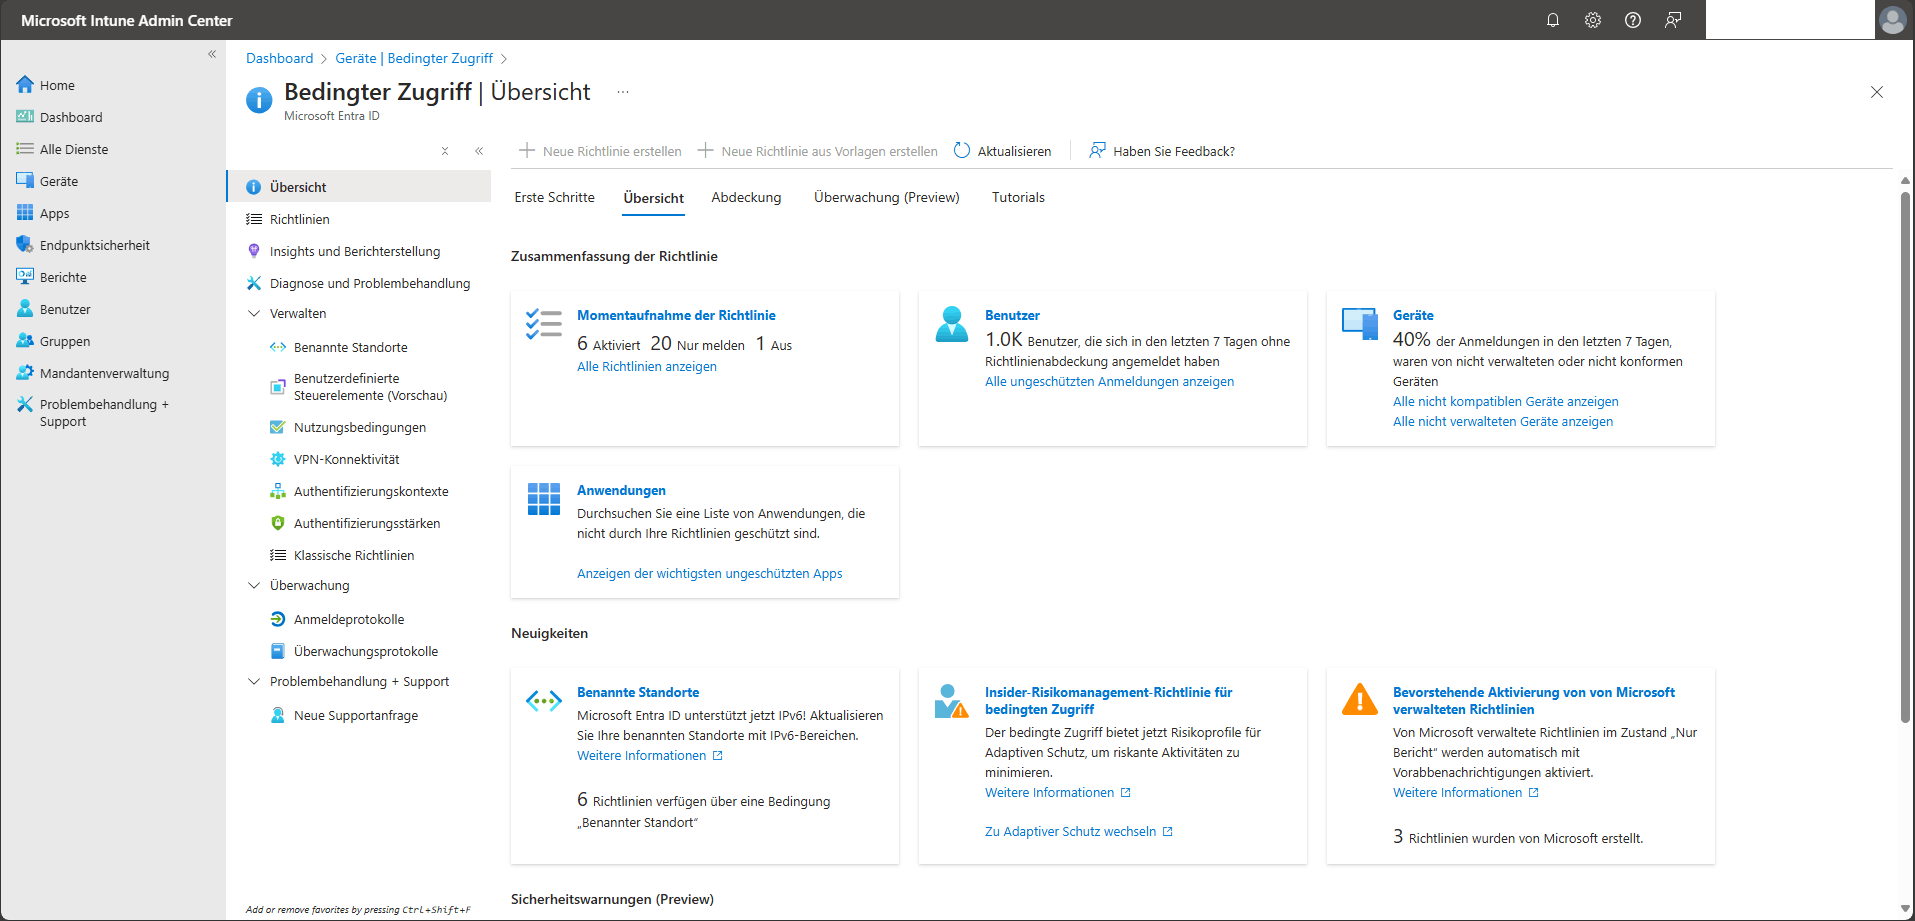
In the "Devices > Overview > Conditional Access" (Conditional Access) section, you can view and manage existing access policies. These policies determine the conditions under which devices or apps are granted access to corporate resources such as email or SharePoint.
Conditional Access enables context-aware access control, for example based on user identity, device status, or other signals. Microsoft Intune can provide the compliance status of devices as a signal for CA, among other things.
6. Manage device configurations via profiles
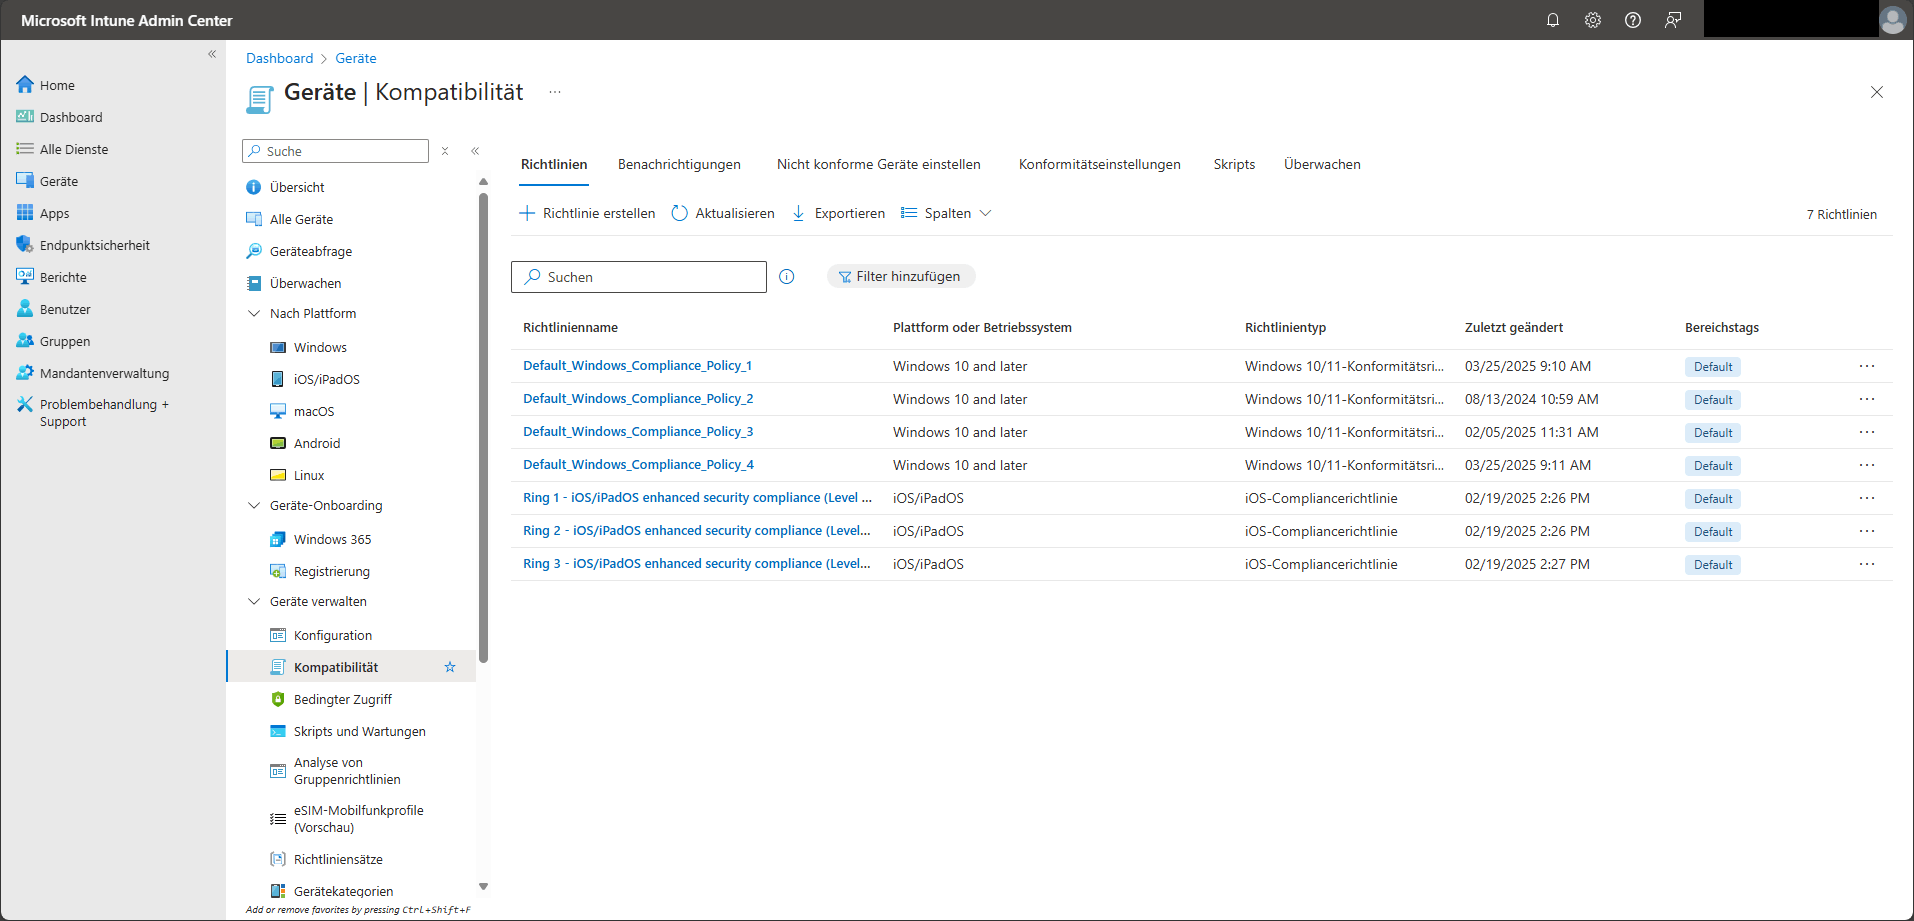
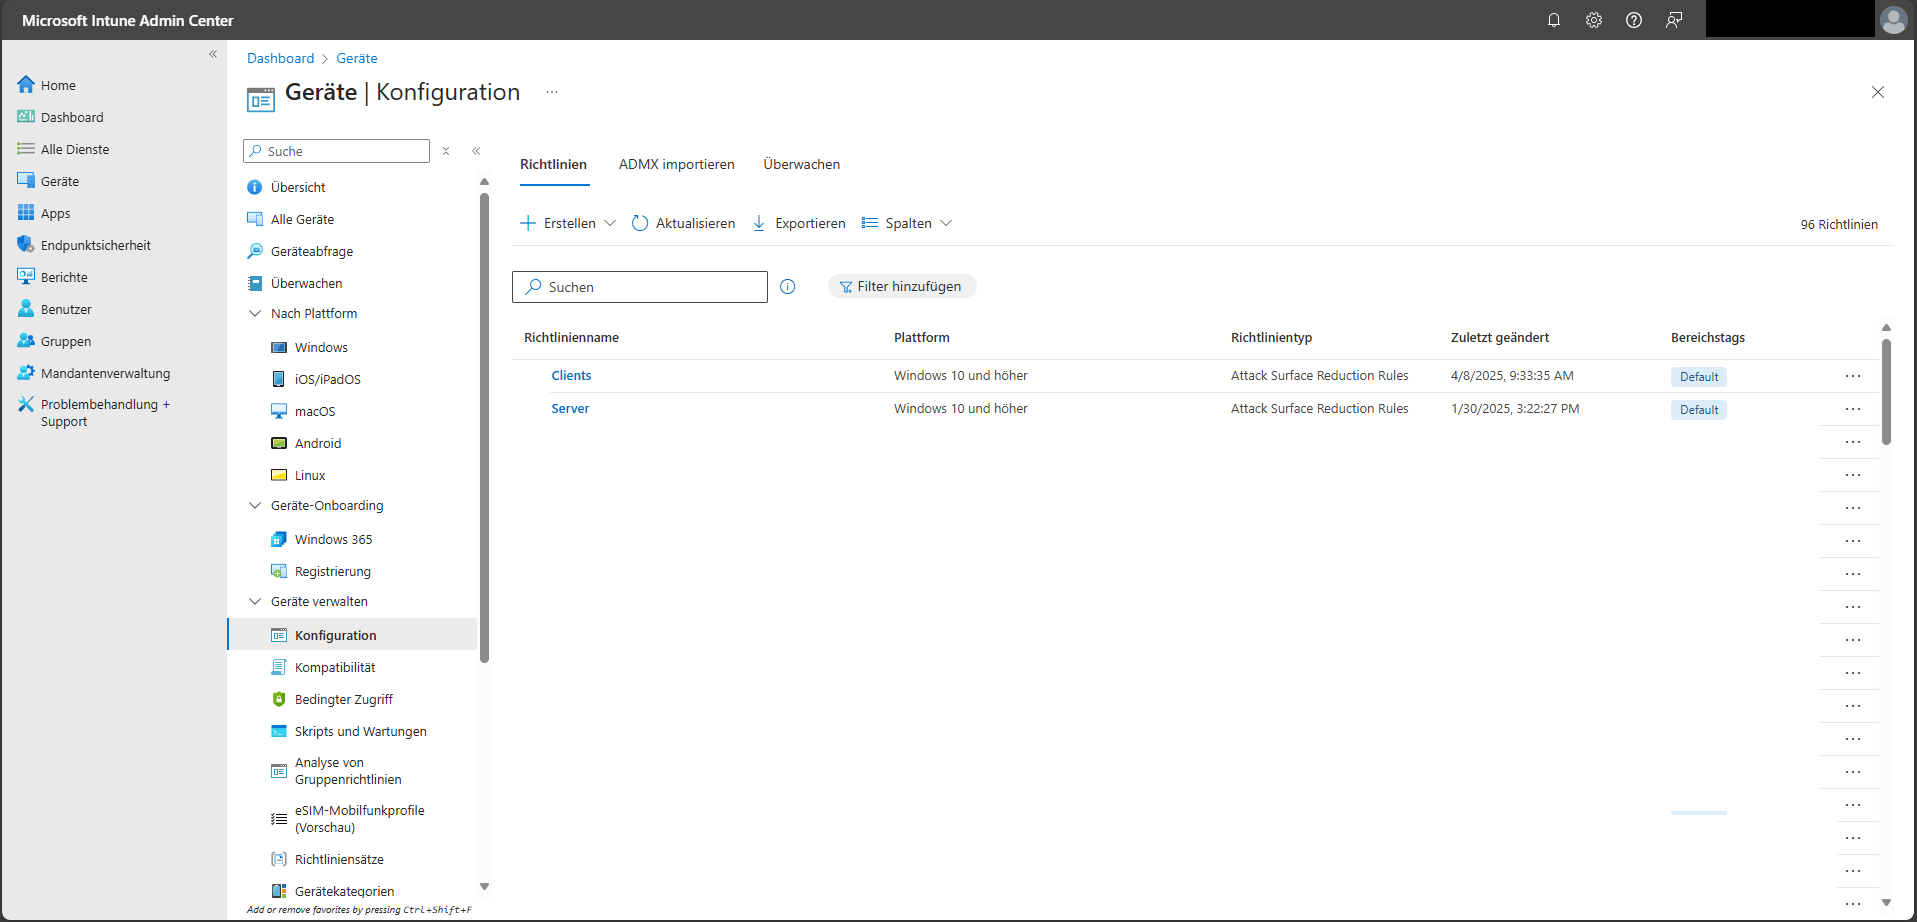
In the navigation pane "Devices > Manage devices > Configuration" you will find all configuration profilescreated in Intune. These profiles contain device settings for enabling, restricting, or disabling specific features – including Wi-Fi, VPN, email accounts, or security-related requirements.
Intune supports profile creation for all common platforms:
- Windows
- macOS
- iOS/iPadOS
- Android
Once created, profiles can be specifically assigned to certain devices or user groups. Changes take effect automatically during the next synchronization.
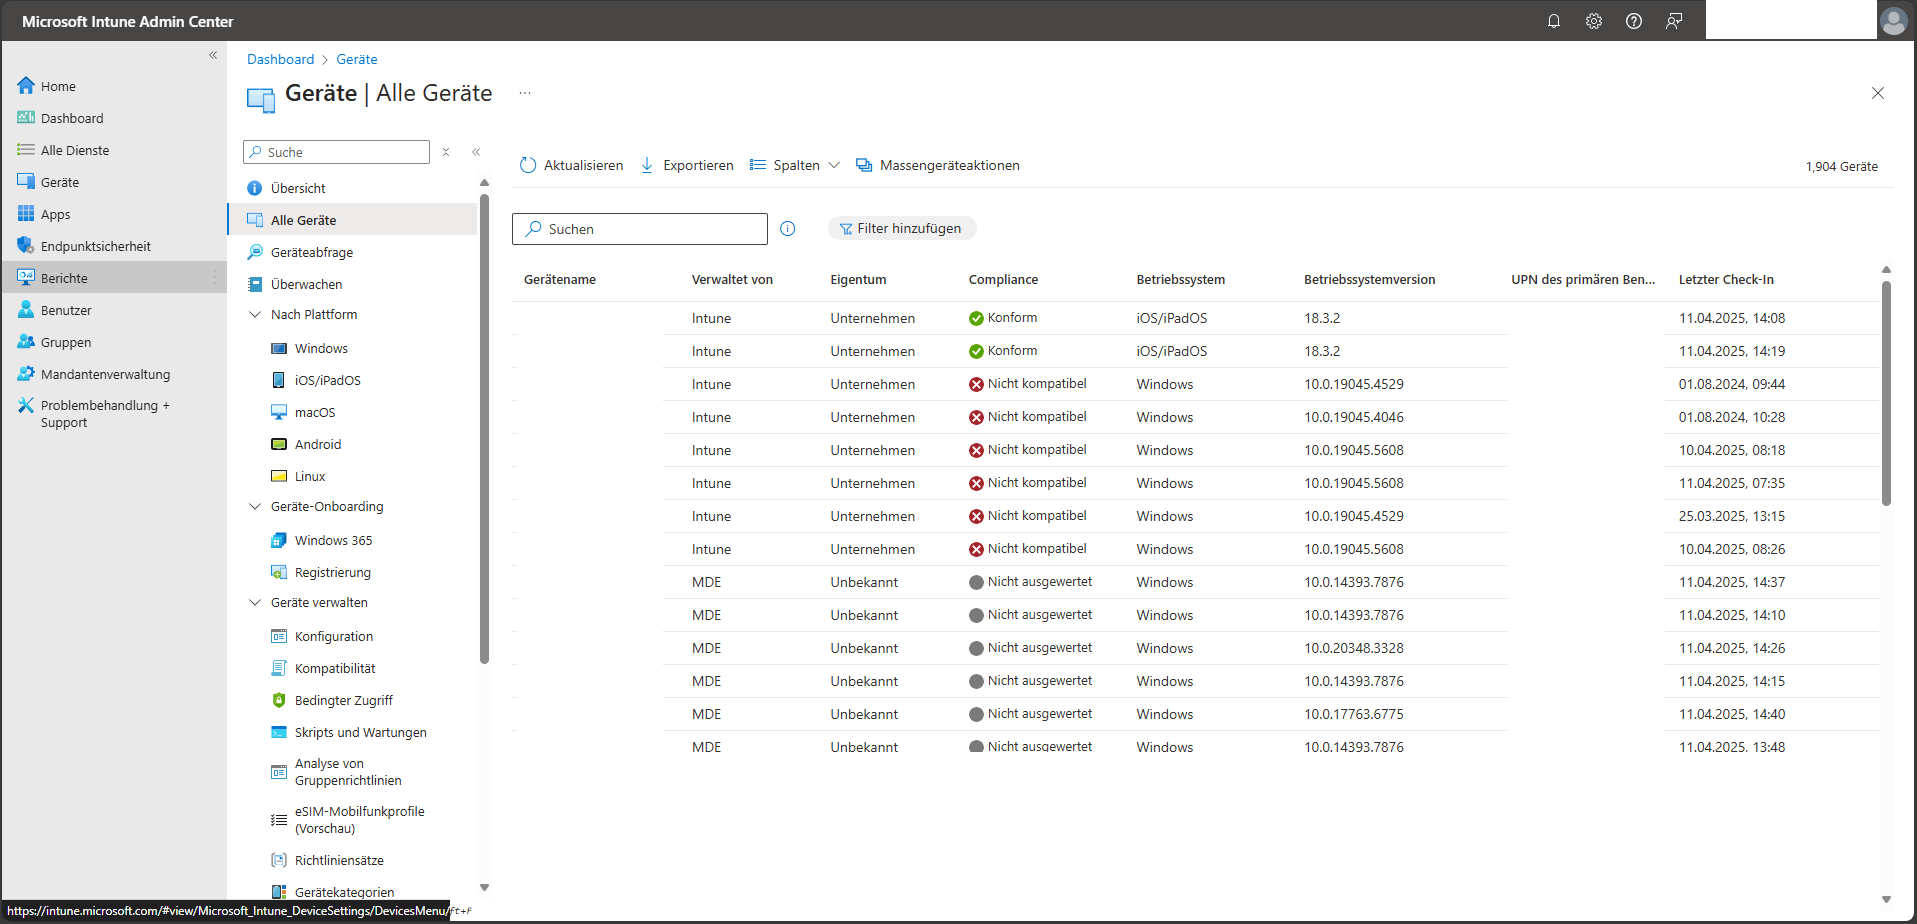
7. Overview of all registered devices
In the "Devices > All devices" displays a complete list of all currently registered devices in the Intune tenant. This overview is essential for daily endpoint management and includes, among other things:
- Device operating system and version
- Compliance status (compliant/non-compliant)
- Time of the last successful check-in
For newly set up Intune instances, this list is initially empty. Once devices are enrolled, it serves as the central hub for analysis, filtering, and targeted management actions.
8. App Overview: Installations and Policy Status
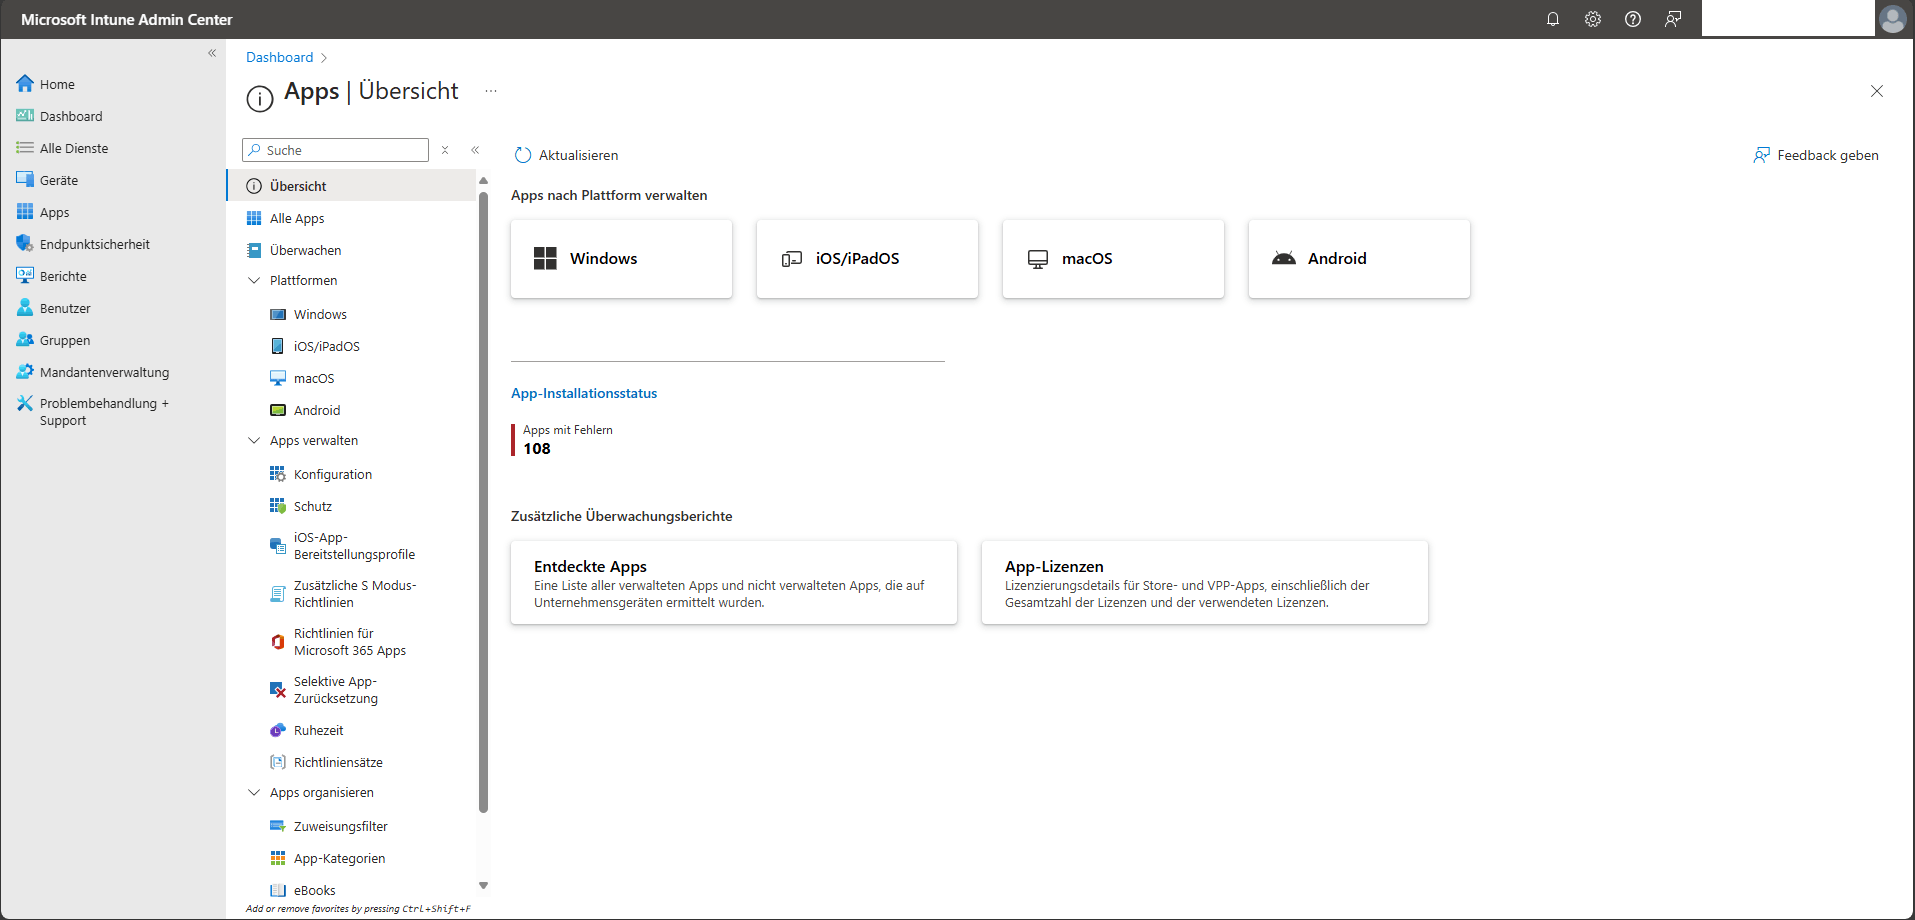
In the "Apps > Overview" menu, you will find a central display of the current app status within the Intune tenant. The view is divided into two main areas:
- Installation status: Shows at a glance which devices or app types have encountered installation errors. This allows you to identify and resolve issues early on.
- App protection policy status: Provides information on which users have been assigned app protection policies – for example, for additional security measures in Office applications on mobile devices.
Furthermore, the overview contains information on the tenant status and the accounts in use. It therefore serves as a central entry point for app management and monitoring.
App protection policies can also be applied to supported devices that are not enrolled in Intune. This is particularly BYOD scenarios relevant.
9. Manage all applications in one place
Under "Apps > All apps" you can see the applications that have been added to the Intune tenant. This is where you can add apps, assign them, and monitor their status. This section is therefore one of the central hubs for software distribution with Intune.
Intune supports a wide range of application types, tailored to each specific platform:
- Win32 applications (.intunewin/.exe/.msi)
- Microsoft Store apps
- Web apps
- Line-of-Business (LOB) apps
- iOS/Android apps via Apple VPP or Managed Google Play
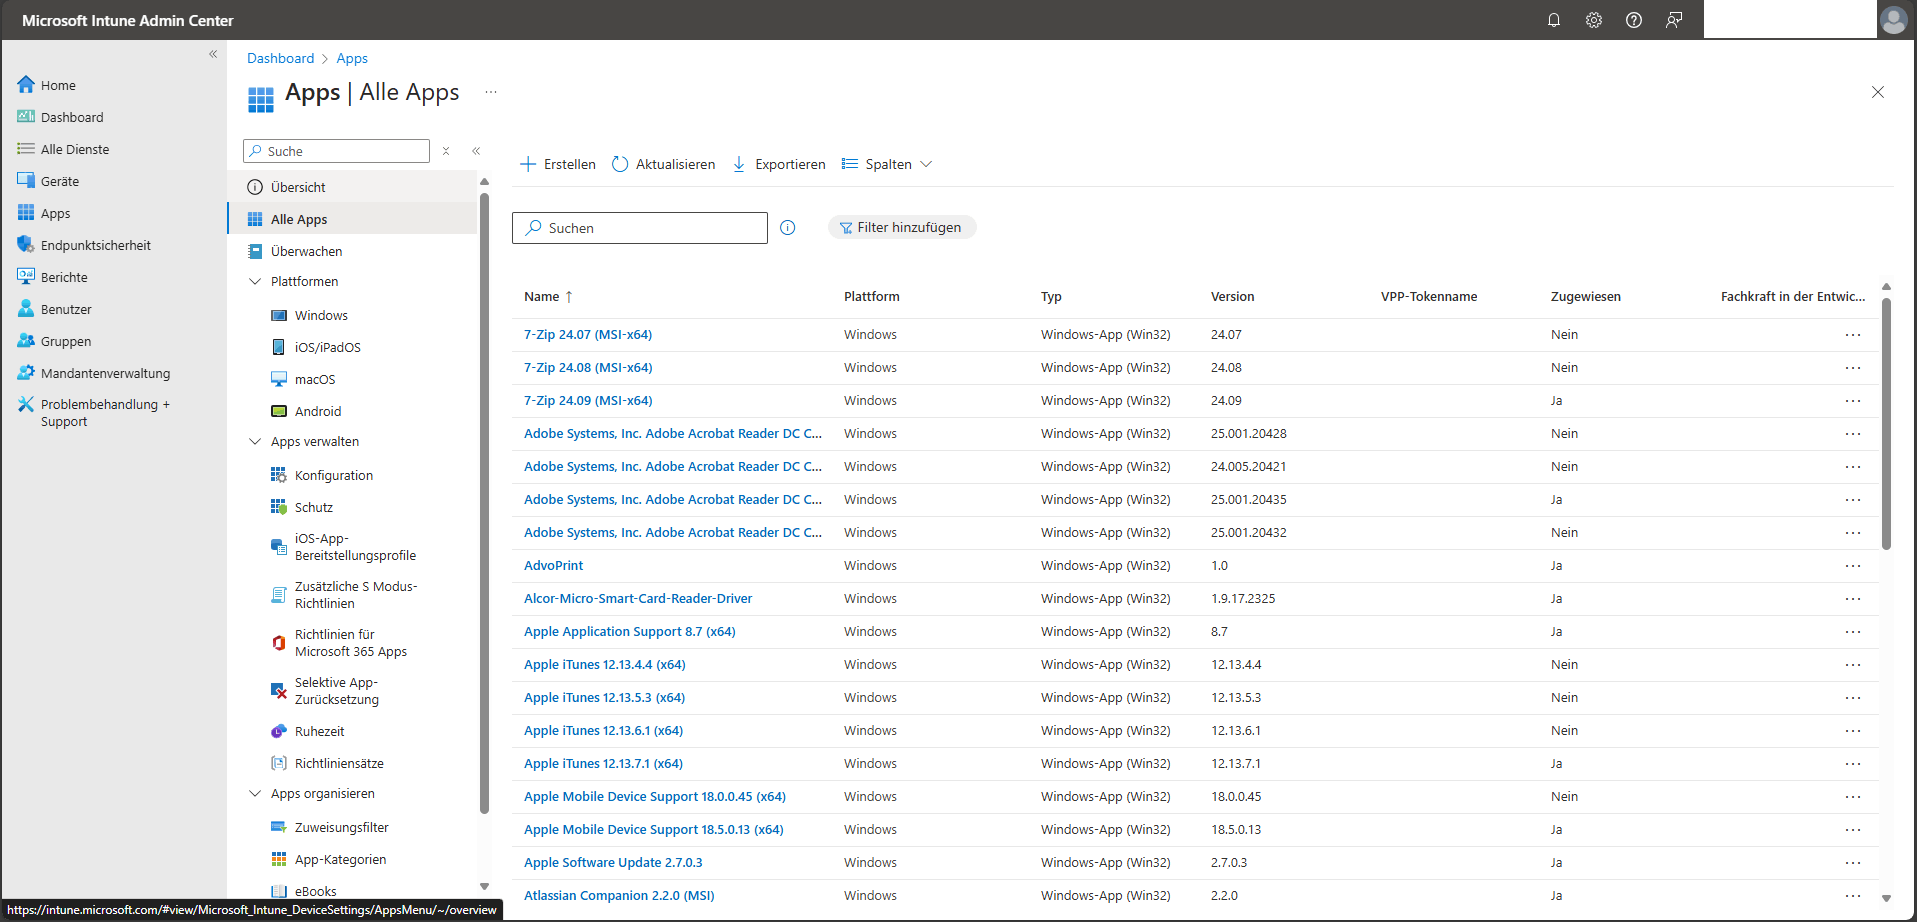
After adding an app , you can assign it to specific user or device groups and monitor the installation status.
10. User overview and permissions management
In the "Users" section, you manage all individuals assigned to the Intune tenant. These users can enroll devices, access company resources, and—depending on their role—perform administrative tasks.
Users can be added in two ways:
- Directly in the Intune admin center
- Synchronized via an on-premises Active Directory instance using Azure AD Connect
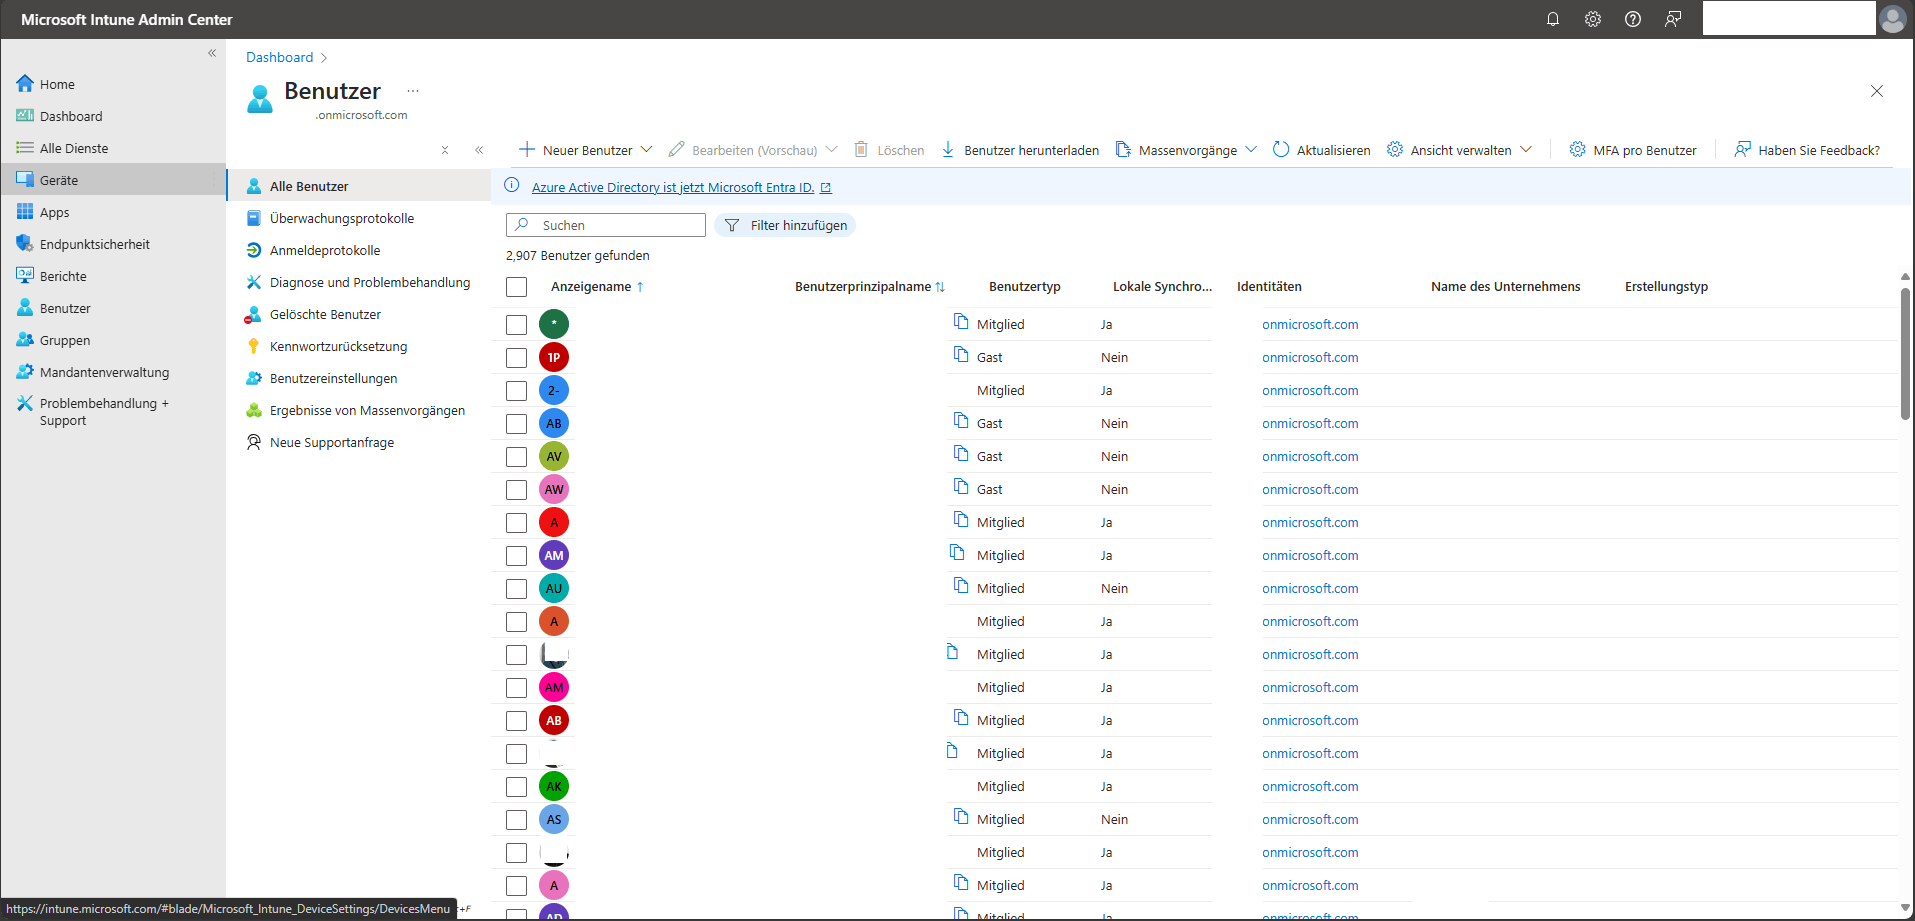
Once added, users can be specifically assigned rights and roles, for example as an Intune administrator, help desk staff, or policy manager.
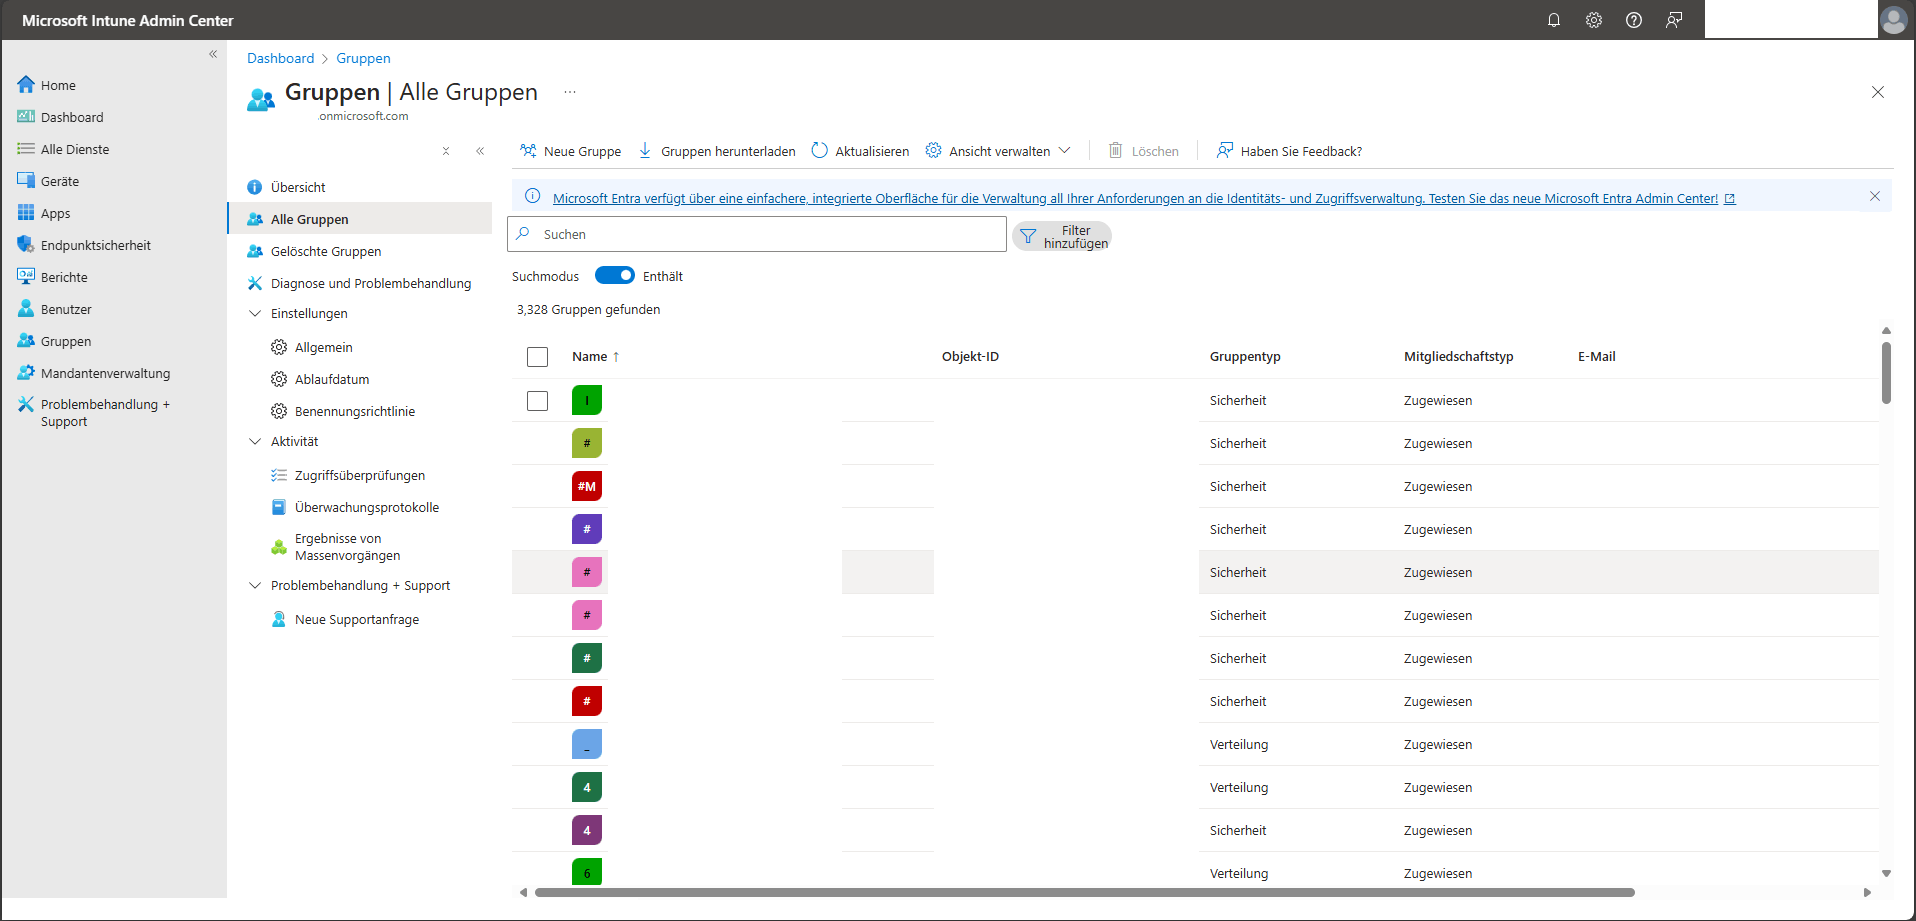
11. Centrally manage and structure groups
In the "Groups" section, all Microsoft Entra groups used within Intune are displayed. These groups serve as the foundation for organizing and managing user and device assignments.
Groups can be set up to meet various requirements – such as by geographic location, organizational unit, or specific device properties. Among other things, they enable:
- centralized policy assignment,
- targeted application deployment,
- as well as structured task distribution in endpoint management.
12. Monitoring tenant status and system health
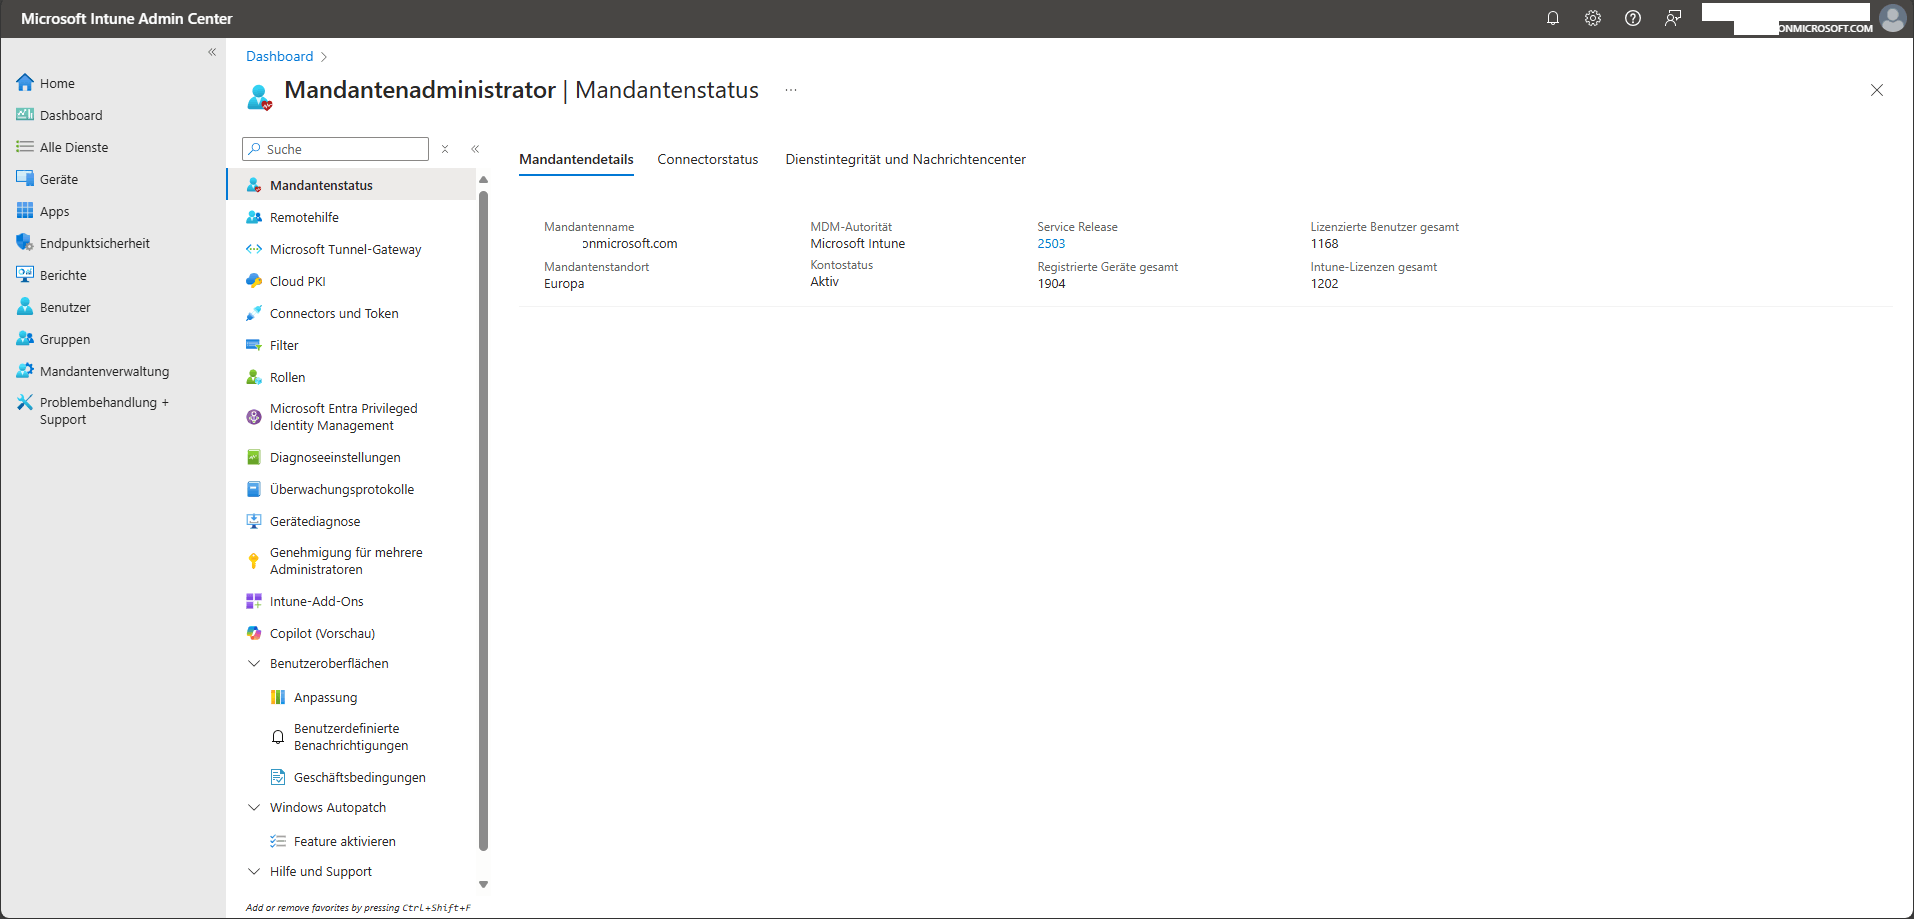
In the "Tenant administration" section, you will find a central overview of the current state of your Intune tenant. The view includes several tabs, such as:
- Tenant details: Information on configuration and general administration
- Connector status: Overview of active connections to other Microsoft services (e.g., Microsoft Defender)
- Service health: Display of the current operational status of Intune services
- Message center: Notifications and alerts regarding planned changes or known issues
This area serves as your first point of contact for troubleshooting or for regularly checking system availability and integrity.
13. Targeted troubleshooting
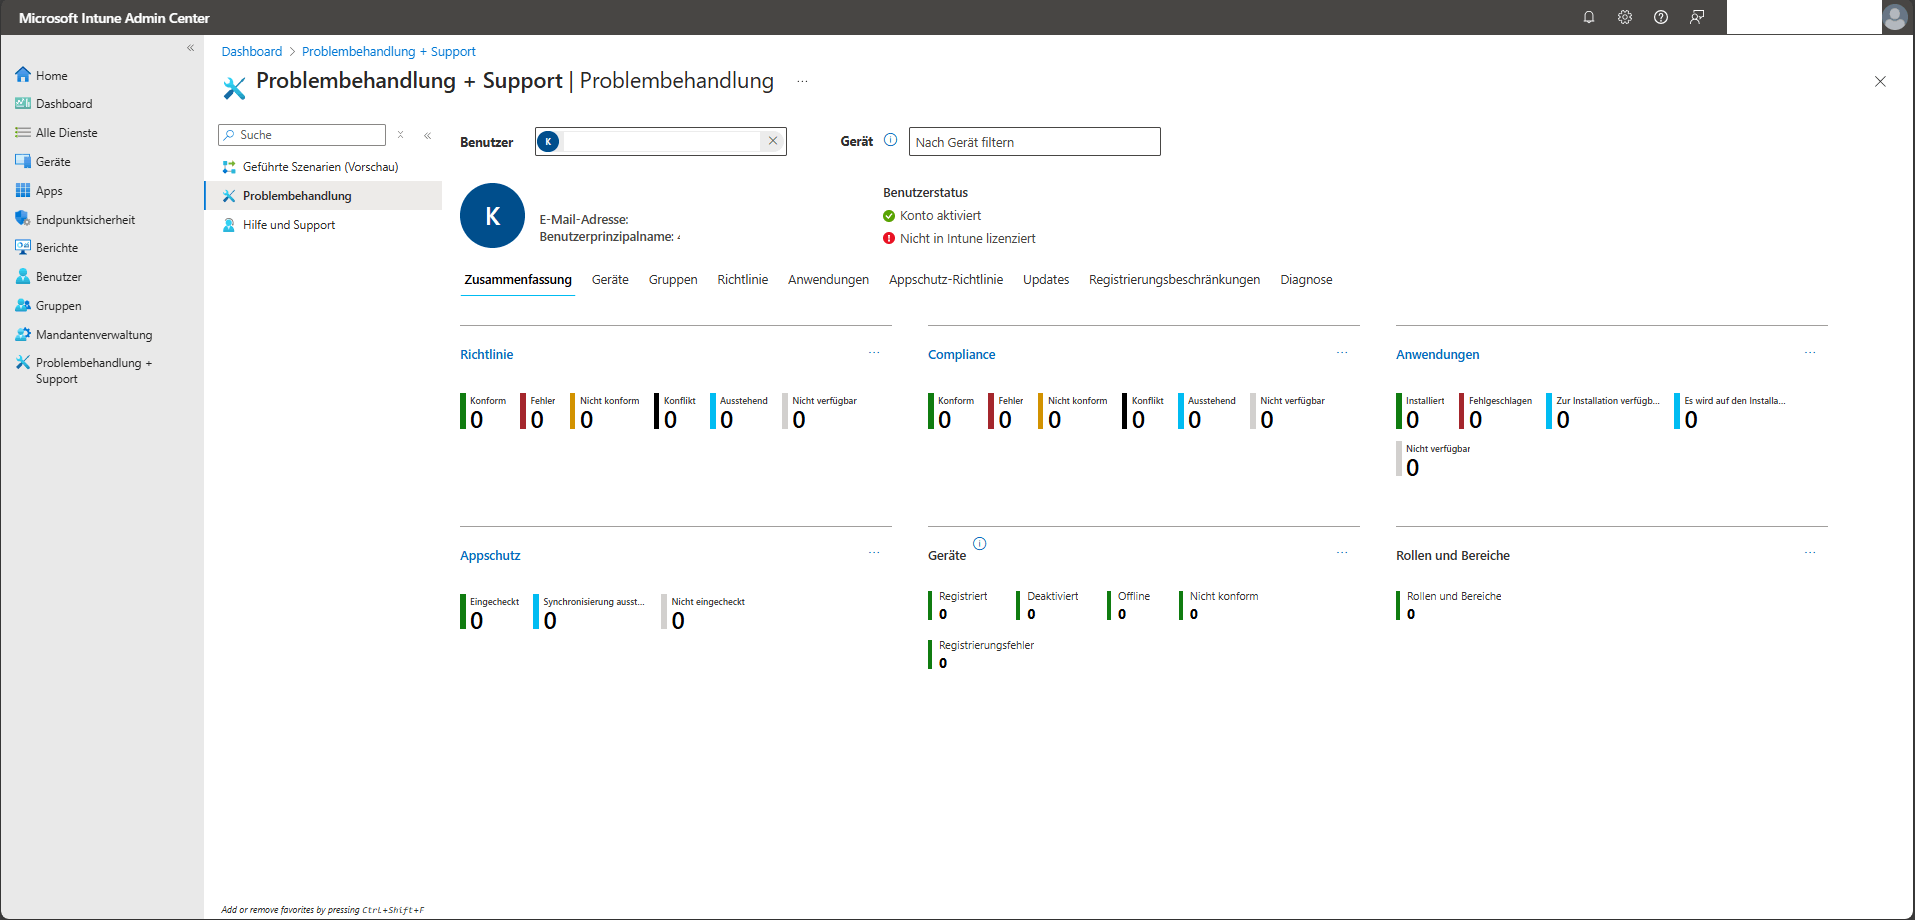
In the Troubleshooting + Support > Troubleshooting you can view status information for individual users or devices. This feature assists with targeted error analysis and is particularly helpful for support cases.
The view is divided into several tabs, including:
- Summary
- Devices
- Groups
- Policy
- Applications
- App protection policy
- Updates
- Enrollment restrictions
- Diagnostics
Each of these tabs provides specific information regarding potential configuration errors, policy violations, or installation issues. This allows causes to be identified and resolved efficiently.
14. Requesting help and creating support tickets
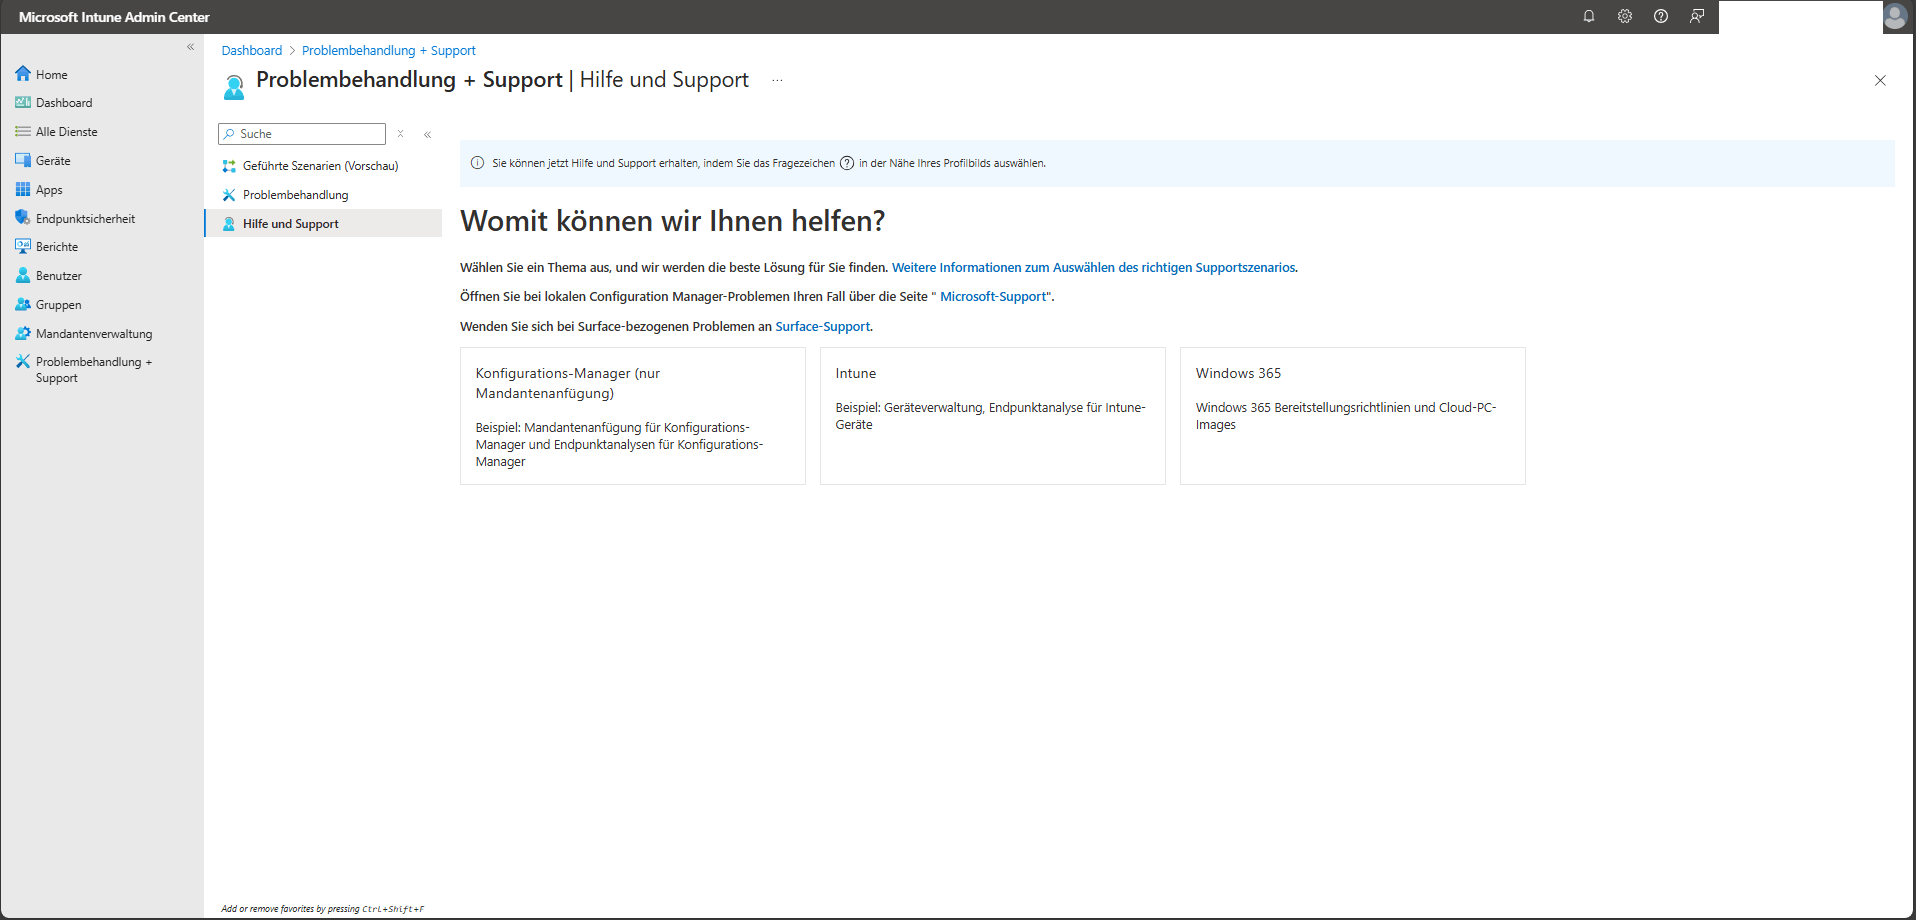
Under Troubleshooting + Support > Help and support the Intune admin center provides direct access to support resources and the ability to create support requests.
This feature allows you to:
- browse troubleshooting solutions and help documentation
- submit support tickets for technical issues
Creating a support ticket requires an appropriate administrator role in Microsoft Entra ID. Supported roles include:
- Service support administrator (recommended – least privileged role)
- Intune administrator
- Global administrator
These roles ensure that only authorized personnel can submit support requests, which enhances security and accountability.
15. Configuring and customizing the Microsoft Intune admin center
The Microsoft Intune admin center can be flexibly adapted to your specific workflows and requirements. Both the dashboard and general portal settings can be configured individually—ideal for IT teams working with different focus areas or roles.
Customizing the dashboard
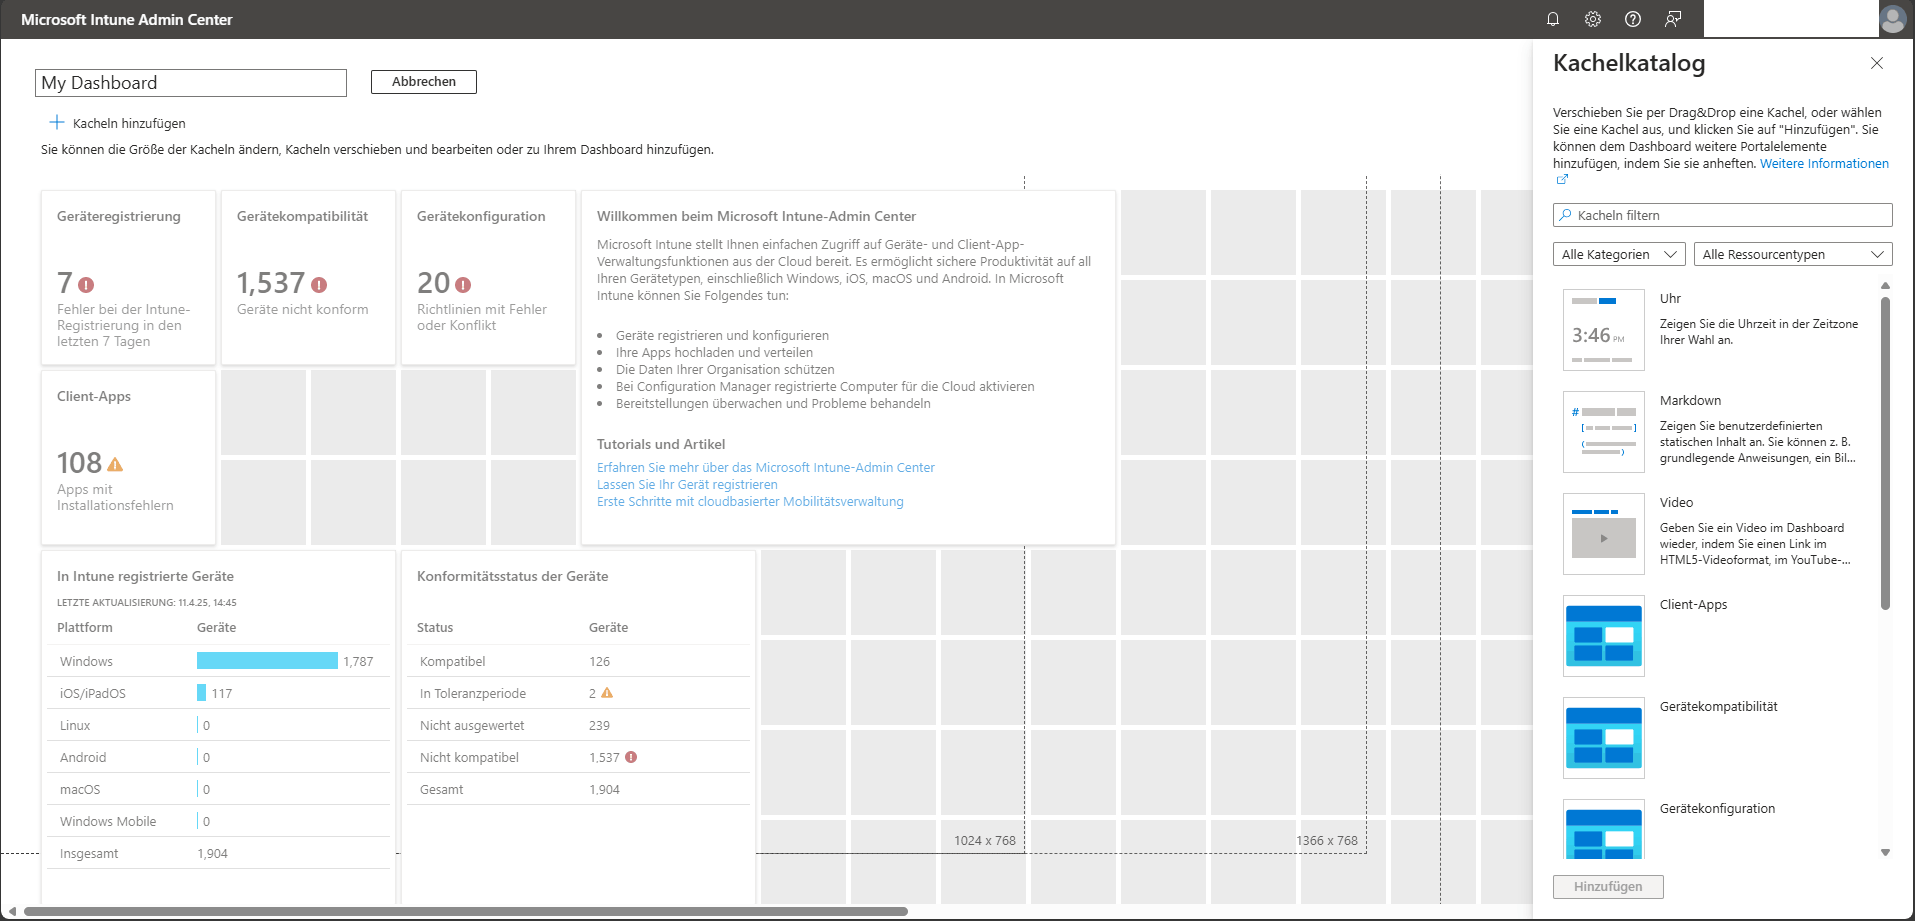
The dashboard serves as a central overview of the status of devices, applications, and policies. It can be designed as a personal workspace—for example, tailored to specific projects or roles. The following options are available:
- Edit existing dashboard: Add, remove, or rearrange tiles
- Create new dashboard: Start with a blank view and select from the tile catalog
- Publish or share dashboards: This allows predefined views to be made available to other team members
The integrated tile catalog offers a variety of visualizations, for example regarding compliance, app status, or device distribution
Change portal settings
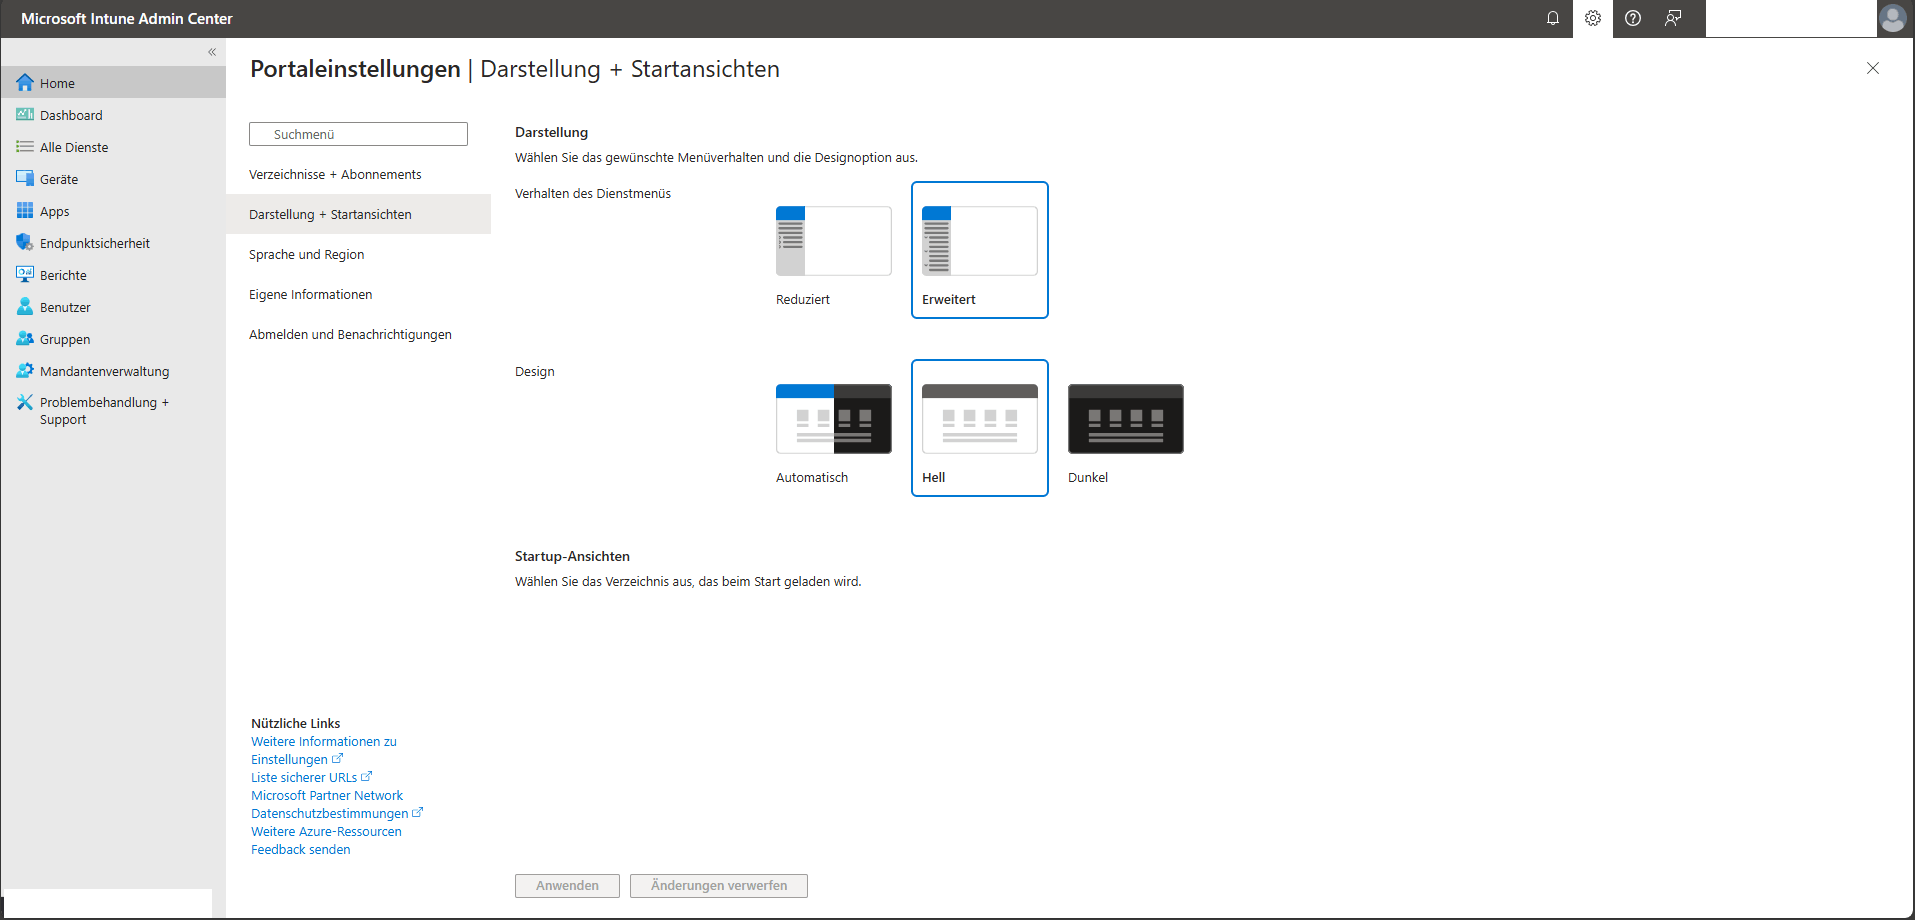
Via the gear icon in the top right corner of the Intune admin center, you can adjust general settings. Configurable areas include:
- Directories & subscriptions
- Appearance & startup views
- Language & region
- Personal user information
- Sign-out behavior & notifications
These options allow for a personalized work environment that significantly simplifies daily tasks and navigation.
4. Best practices for usage
Efficient and secure use of the Intune admin center requires not only technical expertise but also well-thought-out processes and clear guidelines. The following best practices have proven effective in practice:
{{cta-039="/en/dev/components"}}
5. Conclusion
The Microsoft Intune admin center is more than just an administration portal – it is the central control hub for modern endpoint management. With its clear structure, deep integration into Microsoft 365, and versatile features, it enables IT departments to manage devices and applications securely, efficiently, and at scale.
Especially in times of increasing mobility, remote work, and bring-your-own-device srategies, a centralized, cloud-based solution like Intune becomes a decisive success factor for IT security and productivity.
If you need support with the implementation, optimization, or ongoing operation of Intune, we are here to help through our Microsoft Intune consulting.

Dorian has been involved in corporate and IT strategy since 2011. Due to the endpoint security deficiencies of many companies and the information overload, he developed the endpoint strategy. Dorian is co-founder of the “Endpoint Management” expert group at IAMCP e.V.


Years of Experience
Managed Endpoints