Today, corporate resources are no longer confined to the company's own network. Employees access applications and data from home offices, mobile devices, or directly via cloud services. At the same time, the traditional trust model poses a fundamental risk: if attackers manage to penetrate the internal network, access requests there are often less strictly scrutinized, making it easier for them to spread further.
This is exactly where Zero Trust comes in. Instead of assuming trust, access is continuously re-evaluated based on identity, device, risk, and target resource. Microsoft provides various building blocks for this with Microsoft 365, Entra, Intune, and Defender. But how do these work together, and how can a practical Zero Trust strategy be developed from them?
The most important things in brief
- Zero Trust means: no blanket trust. Access requests are evaluated based on identity, device, risk, and target resource – regardless of whether they originate from the internal network or from outside.
- Microsoft implements Zero Trust using several building blocks. These include Entra ID, Intune, Conditional Access, Microsoft Defender, Purview, and Global Secure Access; AI agents and AI resources are also increasingly being added.
- Implementation is carried out in stages. Microsoft recommends starting with identities and endpoints, defining protection levels and access models, and then expanding the environment to include further areas while continuously evaluating them.
- Licensing is part of the planning process. Features such as Entra ID Protection, PIM, Endpoint Privilege Management, or Global Secure Access are not included in every Microsoft 365 license.
Zero Trust step by step: We will work with you to develop a secure strategy for identities, devices, and data in Microsoft 365 and Intune.
1. What is Zero Trust?
Zero Trust is a security strategy where trust is not assumed based solely on a known user, device, or network location, but rather every access request is consistently verified.
Instead, it is checked whether access can be permitted under the current conditions. This applies to access from the corporate network just as it does from a home office or the cloud. Never trust, always verify.
This is how the Zero Trust model differs from the classic perimeter approach. A successful login or access from the internal network is not automatically sufficient. Identity, device health, permissions, target resource, and other risk signals can also be factored into the decision.
Microsoft summarizes its Zero Trust strategy into three core principles:
- Verify explicitly: Access is constantly re-authenticated and authorized based on available signals. These can include identity, location, device health, or risk level. If any such variable changes for a user already accessing corporate resources, they must re-authenticate.
- Use least privilege access: Users, devices, and workloads are granted only the permissions they actually need. Critical rights should be as limited as possible and, where necessary, granted only temporarily.
- Assume breach: Security measures are planned as if an attacker might already have access to part of the environment. Access is therefore strictly limited, activity is continuously monitored, and potential lateral movement is specifically restricted through measures such as micro-segmentation.
Traditional security models long assumed that threats were primarily located outside the network and that internal access was inherently trustworthy. In modern IT environments with cloud services, mobile devices, and hybrid work models, this assumption no longer holds. Today, attackers frequently use stolen identities, insecure devices, or misconfigurations to log in legitimately and then gradually move through the system.
Zero Trust addresses this by replacing implicit trust with continuous validation. Every access request is evaluated based on context and is only granted if identity, device, permissions, and risk level align. This creates a security model that is no longer based on the network perimeter, but on securing every single interaction.
2. Zero Trust Model: Structure and Implementation with Microsoft 365 and Intune
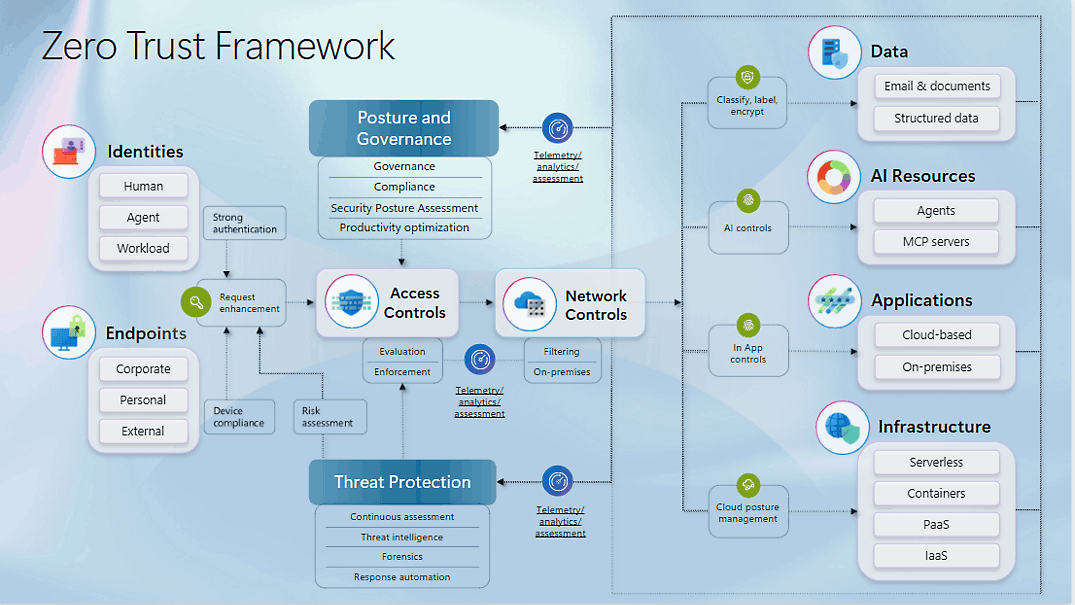
For further analysis, we will use the Microsoft Zero Trust Frameworkas a guide. It divides Zero Trust into various areas and shows how they work together.
Simply put, the framework can be read from left to right: Identities and endpoints provide the context, access controls evaluate and manage access, and network controls secure the connection to data, AI systems, applications, and infrastructure. Security information from these areas then flows back into governance and threat protection.
Our core competencies lie primarily in the first areas of the model: Identity Management, Endpoint Management, Posture and Governance, Access Controls, and Threat Protection. Below, we will take a closer look at these and the other building blocks of the Microsoft Zero Trust Framework.
Identity Management – Securing human and non-human identities
Identities are at the heart of almost every access decision. This includes not only user accounts but also administrators, service accounts, applications, and other non-human identities. The management of these identities and their access is known as Identity and Access Management (IAM) .
With Microsoft Entra ID , Microsoft provides the central platform for identity and access management. MFA or passwordless authentication reduce reliance on traditional passwords, while Entra ID Protection can provide additional risk signals regarding users and sign-ins.
With AI agents, the management of non-human identities is becoming increasingly important. Microsoft now provides dedicated identities for AI agents with Entra Agent ID .
Beyond the identity itself, it is crucial to determine which permissions are assigned to it. With Privileged Identity Management (PIM) , privileged roles can, for example, be activated only when needed and for a limited time. Access Reviews help verify whether existing permissions are still required.
Microsoft Defender for Identity enhances identity protection by detecting and investigating identity-based attacks. This is particularly relevant in environments with on-premises Active Directory or hybrid identities, as it identifies and blocks or alerts on typical attack patterns such as lateral movement, pass-the-hash, or kerberoasting at an early stage.
Endpoints – Centrally manage corporate and personal devices
A known identity alone is not enough for Zero Trust. The device being used can also determine whether access to a corporate resource is permitted, as endpoints are usually the primary target for attacks.
With Microsoft Intune managed endpoints can be configured and evaluated based on defined compliance policies. This can take into account factors such as operating system version, encryption, firewall, or other security settings.
With Endpoint Privilege Management (EPM) the principle of least privilege can also be applied to local administrator rights. This allows standard users to run selected applications or tasks with elevated privileges in a controlled manner, without being granted permanent local administrator rights.
In addition, Microsoft Defender for Endpoint can provide the current device risk. If Defender detects suspicious activity on an endpoint, Intune can incorporate this risk signal into the compliance assessment. As a result, devices exceeding a defined risk level can be classified as non-compliant.
The actual access decision is then enforced via Microsoft Entra Conditional Access . For example, a policy can require that only devices assessed as compliant are permitted to access specific corporate resources. A user may therefore be correctly authenticated and still be denied access if their device does not meet the defined security requirements.
It is not necessary for all end devices to be fully managed by the company. For BYOD scenarios , for example, Intune App Protection Policies can be used to protect corporate data within supported applications and to separate private from business data.
Posture and Governance – Security Status, Compliance, and Optimization
Zero Trust must be continuously reviewed and developed. To achieve this, security status, risks, and progress must be measurable.
With Microsoft Secure Score , the current security status can be evaluated based on concrete recommendations and tracked over time. Microsoft Security Exposure Management goes further by consolidating information on risks, critical assets, attack paths, and security initiatives across various areas of the environment. This allows for the prioritization of particularly relevant vulnerabilities and more targeted planning of improvements.
Additionally, Intune provides information on compliance and configuration issues, for example, while Microsoft Purview supports governance and compliance requirements. The findings can be used to incrementally refine policies and security measures.
Access Controls – Evaluating and enforcing access
The identity, device, and risk signals described above are consolidated here into a concrete access decision. In this process, Conditional Access plays a central role. Policies can, for example, take into account which user is accessing, which device is being used, the current risk level, and which resource is being accessed.
Depending on the result, access can be granted, additional authentication can be required, or access can be blocked entirely. Conditional Access thus forms the link between existing security signals and the actual enforcement of Zero Trust rules.
Threat Protection – Detecting and responding to threats
In addition to access control, Zero Trust also encompasses the detection of and response to active threats. Microsoft Defender XDR consolidates signals and alerts from endpoints, identities, email, cloud applications, and other security areas for this purpose.
Related activities can thus be viewed as unified incidents and investigated across different areas. Automated investigation and response capabilities further assist in containing detected threats.
Network Controls – No more "internal trust"
Even an internal network or an existing VPN connection is no longer considered sufficient proof of trust in the Zero Trust model. The decisive factor remains which resource an identity is permitted to access and under what conditions.
For this, Microsoft provides Global Secure Access provides its own Security Service Edge solution. This includes Microsoft Entra Internet Access and Microsoft Entra Private Access. Private Access enables Zero Trust Network Access (ZTNA) for private applications and resources, allowing it to supplement or partially replace traditional VPN-based access scenarios.
With Global Secure Access, the previously described access rules can be extended to the network level. This allows access to be more tightly bound to specific applications and resources, rather than granting users broad, blanket access once a network connection is established.
Data – Protecting structured & unstructured information
Data itself must also be protected within the Zero Trust model. With Microsoft Purview Information Protection , sensitive content can be classified and labeled, as well as encrypted and restricted in its usage based on defined policies.
This ensures that protection remains tied to the information—for example, by setting requirements for who is permitted to open, forward, or print documents.
AI Resources – Securing agents and AI systems
AI agents and connected AI services introduce new resources and access paths into the Zero Trust model. These include, for example, agents or MCP servers that access corporate data, applications, and other systems.
For identity and access control, Microsoft provides Entra Agent ID to offer dedicated identities for AI agents. Microsoft Purview Data Security Posture Management (DSPM) complements this on the data side: the solution provides transparency regarding deployed AI apps and agents, sensitive interactions, and potential data risks, while supporting the implementation of appropriate security policies.
Applications – Securing SaaS and on-premises
Applications must also be integrated into the Zero Trust model. Microsoft Entra ID supports modern authentication and single sign-on for cloud applications. With Microsoft Entra Application Proxy you can also provide external access to selected on-premises web applications.
Microsoft Defender for Cloud Apps provides visibility into SaaS applications in use and helps identify unauthorized cloud services and risky activities, as well as enforce policies for their use.
Infrastructure – Control over Cloud & On-Premises
Infrastructure and workloads are also part of the Zero Trust model. This includes cloud resources as well as on-premises servers and hybrid or multi-cloud environments.
Microsoft Defender for Cloud helps assess the security posture of resources and workloads, detect misconfigurations and vulnerabilities, and implement additional protective measures. Depending on the environment, this includes, for example, virtual machines, containers, databases, and serverless workloads in Azure, as well as connected AWS, GCP, and on-premisesresources.
Features such as security recommendations, workload protection, and just-in-time access help reduce risks and manage administrative access more effectively based on the principle of least privilege.
3. Roadmap for implementing Zero Trust with Microsoft 365
Implementing Zero Trust is a strategic transformation process, and Microsoft provides a highly detailed and practical roadmap.
This roadmap guides IT managers step-by-step through every phase of Zero Trust adoption—from securing identities and device management to protecting data, networks, and applications.

Determining the starting point and protection requirements
It all begins with an assessment. Which users and devices are accessing which resources? Where are the most sensitive data and applications located? Which privileged accounts exist, and which devices are currently unmanaged or only partially managed?
In addition to the Zero Trust Adoption Framework, Microsoft now also provides an automated Zero Trust Assessment . It checks numerous configurations within a Microsoft tenant and maps potential improvements to the various Zero Trust domains.
While such an assessment provides a starting point, actual prioritization should be based on the risks and business processes that are most relevant to your specific organization.
Securing identities first
Since identities are the starting point for many access requests, identity management should be addressed early in your Zero Trust strategy.
This includes, for example:
- Multi-factor or passwordless authentication
- Protection of privileged accounts
- Reviewing existing permissions
- Detecting risky users and sign-ins
- initial Conditional Access policies
A controlled rollout is highly recommended, especially for Conditional Access. Policies should be tested first, exceptions and emergency accounts accounted for, and then gradually tightened. Microsoft continues to describe Conditional Access as the central policy engine for Zero Trust and recommends a planned implementation rather than individual, uncoordinated policies.
Managing and assessing endpoints
The next step is to gain visibility into the devices accessing corporate resources. Only then can device health be factored into access decisions.
With Microsoft Intune, endpoints can be registered, configured, and assessed via compliance policies. Together with Microsoft Defender for Endpoint risk signals can also be taken into account.
For Zero Trust on endpoints, Microsoft now explicitly recommends a multi-stage approach. Security begins with basic protective measures and is gradually expanded to include enrollment, device configuration, compliance, threat detection, and advanced data protection.
This means that every client does not have to reach the final target state immediately. It is more important to create a robust foundation upon which access policies can later reliably distinguish between known, compliant, and potentially compromised devices.
Defining access models
Once identities and endpoints are sufficiently visible, concrete Zero Trust access models can be defined. This should determine not only who is allowed to access a resource, but also under what conditions.
In its recommendations for identity and device access, Microsoft distinguishes between three protection levels: Starting point, Enterprise, and Specialized security. The higher the protection requirement, the stricter the demands placed on identity, device, and access.
Simplified for your own environment, this can mean, for example:
- Starting point: basic protection for regular users and resources
- Enterprise: higher requirements for sensitive applications and data, such as a compliant device and stricter risk-based access rules
- Specialized security: particularly restrictive requirements for highly sensitive, regulated, or high-value resources
The specific Conditional Access policies should then be aligned with the respective protection requirements. This creates a tiered policy structure rather than a one-size-fits-all rule for the entire company.
Include applications, data, network, and infrastructure
Once identity and endpoints are covered, other areas can be integrated step by step. These include, for example, SaaS applications, sensitive corporate data, private applications, cloud resources, and on-premises infrastructure.
Depending on the environment, tools such as Microsoft Purview, Defender for Cloud Apps, Defender for Cloud, or Entra Private Access can be used for this purpose.
It is important not to view Zero Trust solely as a cloud project. Existing on-premises applications and hybrid infrastructures can also be part of the strategy. Microsoft itself points out that the specific path to Zero Trust implementation varies depending on the existing infrastructure and requirements.
{{cta-038="/en/dev/components"}}
4. Challenges in Zero Trust implementation
Zero Trust can rarely be built in a completely new IT environment. Existing applications, legacy permissions, and heterogeneously managed devices must therefore be taken into account during Zero Trust implementation. This is often where the greatest effort lies.
- Legacy applications and hybrid environments: Older applications often do not support modern authentication. This makes direct protection via Entra ID and Conditional Access more difficult. However, many of these systems can still be integrated into a Zero Trust model using solutions like Entra Application Proxy and Entra Private Access.
- Conditional Access must be introduced carefully: Overly restrictive policies can lock out users or administrators. Therefore, new rules should first be tested in report-only mode or with pilot groups. Emergency access accounts must always remain excluded.
- Performance and network architecture: Additional network-level security controls can introduce new traffic paths and, consequently, additional latency, depending on the architecture. This applies, for example, to SSE, proxy, or TLS inspection scenarios. Therefore, network performance and user experience should be tested and monitored during rollout. Solutions such as Global Secure Access offer optimized routing mechanisms for this purpose and can reduce unnecessary backhauling.
- Zero Trust is an ongoing process: Zero Trust does not end with implementation. Policies, roles, and permissions must be regularly reviewed and adjusted to ensure that security and productivity remain in balance.
5. Conclusion: Implementing Zero Trust step-by-step
Zero Trust is not a single tool, nor is it a project that is completed after a one-time implementation. The key is the interaction between identities, endpoints, applications, data, and clearly defined access rules.
You don't need to overhaul your entire environment at once to implement this. In Microsoft environments, it makes sense to start with identities and endpoints, gain visibility into existing access, and then gradually introduce Conditional Access and other protective mechanisms. Microsoft's deployment plan, mentioned earlier, is a helpful resource for this.
Anyone looking to implement Zero Trust should first determine which resources require the most protection, which signals are already available, and where any blind spots currently exist.
Licensing should also be considered early on. Some of the features mentioned are not included in every standard Microsoft 365 license. The specific Entra, Intune, or security licenses required depend on the desired functionality and your existing environment.
It quickly becomes clear how complex implementing Zero Trust can be. SOFTTAILOR is here to help you Zero Trust with Microsoft 365 implement it effectively – from developing a strategy tailored to your Microsoft environment to the technical implementation.

Dorian has been involved in corporate and IT strategy since 2011. Due to the endpoint security deficiencies of many companies and the information overload, he developed the endpoint strategy. Dorian is co-founder of the “Endpoint Management” expert group at IAMCP e.V.


Years of Experience
Managed Endpoints